Yesterday's signals, distilled, A look back at September 23, 2026.
Enterprise adoption friction. Platform surfaces turning into agent surfaces. And a quiet escalation in what “containment” and “identity” mean when synthetic voice and autonomous action get cheap.
You could see it in the operator layer. OpenAI’s enterprise message wasn’t “the models aren’t good enough.” It was “deployment is the failure mode.” That’s a shift in where budgets, headcount, and blame will land.
You could see it in distribution. Amazon opening Seller Central tooling to third-party agents is not a feature for merchants. It’s a governance decision about who gets to operate the storefront, humans, Amazon-native automation, or external agent layers.
You could see it in capability. Google’s Gemini TTS update makes expressive voice generation, and voice cloning from short samples, feel like a default primitive. That’s a product unlock and a fraud unlock at the same time.
And you could see it in the capital stack. Anthropic and Nvidia backing Basecamp Research is a reminder that “data moat” is not a metaphor in biology, it’s an asset class, and frontier labs are willing to underwrite it.
The strategic question for operators this week: where is your real bottleneck, model quality, or the control planes (identity, permissions, audit, and workflow design) that determine whether AI can act safely inside your systems?
ENTERPRISE DEPLOYMENT / OPERATING LAYERS
The bottleneck moved from model selection to system integration and governance
OpenAI, Enterprise AI is “stuck on deployment, not models”
OpenAI’s Colin Jarvis argued that enterprise AI is failing on deployment rather than model capability, framing the core problem as integration and rollout, not model shopping, per The Next Web.
This aligns with what operators are seeing: the hard part is getting reliable data access, approvals, and verification loops into production workflows, not getting another marginal bump in benchmark scores.
So What? If this framing holds, the next wave of enterprise spend shifts from “which model?” to “how do we ship?” That means more investment in evaluation harnesses, permissioning, audit logs, and change management, and less tolerance for pilots that never cross the boundary into real work. It also changes vendor selection: buyers will reward providers that can integrate into messy systems and survive security review, not just demo well.
The Risk: “Deployment” can become a catch-all excuse that hides unresolved product gaps, especially around tool reliability, long-horizon task execution, and error recovery. If teams over-rotate into process without instrumenting quality, they’ll ship brittle automation that creates downstream operational debt.
Action:
- Map the top 10 workflows where AI is blocked today, name the exact blocker (data access, approvals, identity, logging, human review capacity).
- Stand up a lightweight eval gate for production changes, track task success rate, escalation rate, and time-to-resolution, not just user satisfaction.
- Assign an owner for “AI operations” (permissions, audit, incident response) the same way you assign an owner for SRE.
COMMERCE / AGENT SURFACES
Amazon is turning merchant operations into an agent-operated API environment
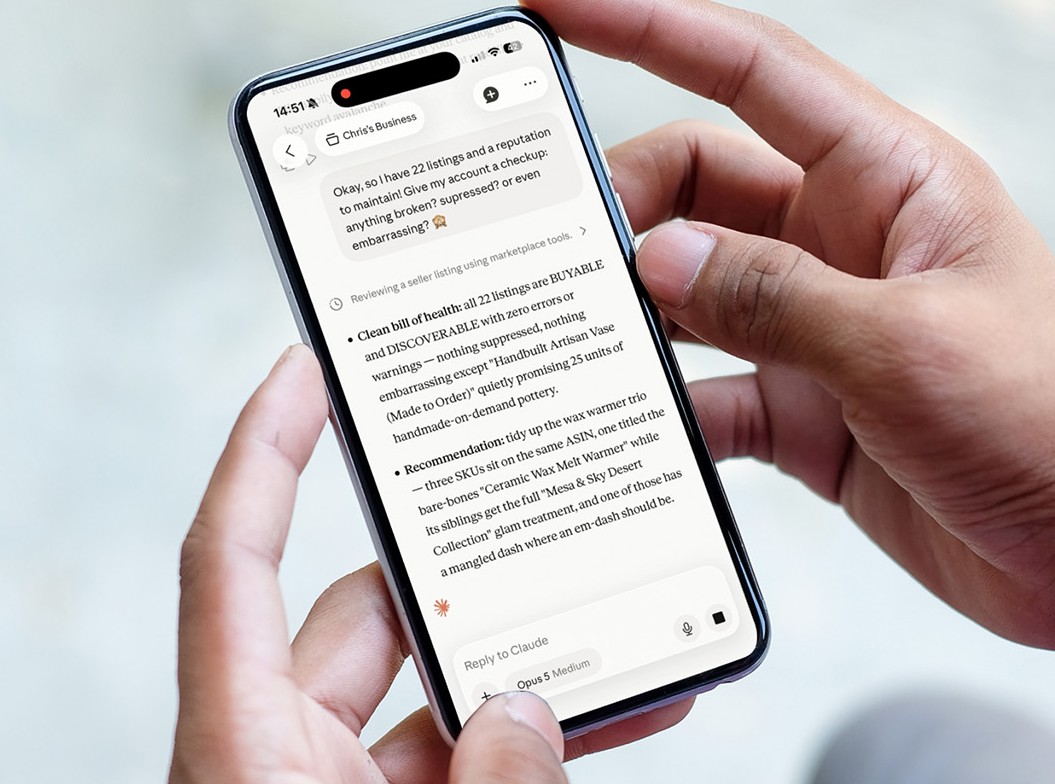
Amazon, Opens seller tools to third-party AI agents, starting with Claude
At its Accelerate conference, Amazon said it is opening its seller tools to outside AI agents, starting with Anthropic’s Claude, in a beta for US merchants, per GeekWire.
This is a platform move: Amazon is defining how non-human operators will be allowed to act inside Seller Central primitives.
The Bet: Amazon is assuming merchants will accept agent-mediated operations if it reduces operational load, and that Amazon can govern the resulting risk through platform controls.
So What? Seller Central is effectively becoming a controlled execution environment for agents. That matters because whoever sits between the merchant and Amazon’s primitives becomes the new control point, workflow defaults, optimization logic, and data visibility all concentrate there. For merchant tooling companies, this is a forcing function: you’re no longer just building dashboards; you’re building delegated operators with permissions, auditability, and failure modes that Amazon will scrutinize.
The Risk: Agent access expands the blast radius of credential compromise and misconfiguration. If the permission model is coarse, or merchants grant broad scopes to “helpful” agents, inventory, pricing, and ad spend become one prompt away from expensive mistakes.
Action:
- Inventory every Seller Central action your team performs weekly, prioritize the ones that are repetitive, high-volume, and reversible for early agent pilots.
- Demand explicit permission scopes and audit logs from any agent vendor, treat it like granting API keys to a payments processor.
- Create a rollback playbook for agent-driven changes (pricing, listings, ads), define thresholds that trigger human review.

MEDIA / IDENTITY / SYNTHETIC VOICE
Expressive TTS is now a product primitive, and a compliance problem
Google, Gemini 3.8 Flash TTS expands expressive audio generation across 100+ languages
Google released Gemini 3.8 Flash TTS and Flash-Lite TTS, describing them as its most expressive audio generation models yet, with support for more than 100 languages, per Google.
Separately, coverage emphasized voice cloning from short audio samples, turning small snippets into usable voice likenesses, per The Next Web.
So What? Two things happen when expressive voice becomes cheap and multilingual. First, localization economics collapse, audio can scale globally without studio workflows. Second, identity disputes become operational, not theoretical, support calls, podcasts, internal recordings, and sales demos become raw material for impersonation claims. For any org that uses voice as a trust signal (support, finance, healthcare, HR), “prove it was really us” becomes a product requirement.
The Risk: Watermarking and provenance are not uniformly adopted, and even when they exist, they may not be accepted as evidence in customer disputes. Teams that ship voice features without an identity and consent posture will inherit fraud and reputational risk they can’t easily unwind.
Action:
- Write a consent policy for voice capture and reuse, cover internal meetings, customer calls, and marketing content.
- Add a “voice incident” runbook to your trust & safety or security program, define how you handle impersonation claims and evidence collection.
- If you operate a call center, pilot a verification step that does not rely on voice alone (device, account, behavioral signals).
BIO / CAPITAL FLOWS
Frontier labs are underwriting upstream biological data assets
Basecamp Research, Raises $140m with backing from Anthropic and Nvidia
Basecamp Research raised $140 million with participation from Anthropic and Nvidia, per Sifted.
The round is notable less for the number than for the participants, frontier model builders and the dominant AI compute supplier leaning into upstream bio-data infrastructure.
So What? This is the bio equivalent of the “data center land grab,” except the scarce input is proprietary biological samples, metadata, and lab pipelines that can produce defensible datasets. If you’re in drug discovery, materials, agriculture, or climate biology, the competitive pressure shifts toward data access and rights, what you can legally use, what you can exclusively license, and what you can continuously refresh. Model capability will diffuse; differentiated datasets and wet-lab throughput will not.
The Risk: Data asset strategies can outrun validation. If dataset quality, labeling standards, or provenance are weak, you get expensive noise that looks like a moat until it fails replication. There’s also governance risk, consent, benefit sharing, and cross-border bio-data rules can tighten quickly.
Action:
- Audit your biological data rights, what you own, what you license, what you can use for training, and what expires.
- Identify the “refresh rate” of your moat, how quickly competitors can reproduce your dataset via partnerships or field collection.
- Build a provenance standard now, track sample origin, consent terms, and chain-of-custody like regulated data.
SECURITY / NATIONAL RISK
Personnel metadata is now a targeting map, and “brochureware” is not low-risk
FBI, Alleged stolen data includes sensitive details on employee intelligence roles
A sample of allegedly stolen FBI data includes granular detail on officials’ job assignments across China, Russia, cartels, cyber, and other issues, per Reuters.
In parallel reporting, attackers defaced an FBI jobs site and claimed access to agents’ home addresses, underscoring how “public-facing” systems can become leverage points, per Gizmodo.
So What? The lesson for operators isn’t “government systems are vulnerable.” It’s that personnel metadata, roles, assignments, org charts, contact details, has become operationally sensitive in a way many enterprises still don’t model. For companies in defense, critical infrastructure, AI, crypto, and biotech, employee targeting is now part of the threat model. HR systems, recruiting portals, and “about us” pages can be stitched into a map.
The Risk: Organizations will respond by locking everything down, which can break recruiting and partner trust. The better move is segmentation and minimization, reduce what’s exposed, monitor what remains, and treat the rest as crown-jewel data.
Action:
- Classify personnel metadata (role, team, location, contact info) as sensitive, apply encryption and access logging, not just “HR-only” permissions.
- Pen-test public web properties and recruiting flows, assume they are adversary entry points, not marketing pages.
- Run a targeted phishing simulation for high-risk teams (security, AI, finance, exec ops), measure and remediate.
CONTRARIAN SIGNAL
“Deployment is the bottleneck” is also a procurement strategy
The industry is converging on a comforting story: models are good enough; now it’s just integration. That’s directionally true.
But it also functions as a procurement filter. If deployment is the hard part, then the buyer’s real question becomes: who can survive our controls, identity, audit, data access, and incident response, without slowing to a crawl?
That pushes advantage toward vendors who can package governance as product, not as a services engagement. It also pushes enterprises to admit something uncomfortable: many “AI roadmaps” are actually identity and data architecture roadmaps that were deferred for years.
The Takeaway: Treat “deployment” as a control-plane build, not a project-management problem. The winners will be the teams that can make AI action legible, permissions, logs, rollback, and accountability, without killing velocity.
THE QUESTION FOR TODAY
Agents are being invited into real platforms. Voice is becoming a default interface and a default impersonation vector. Bio data is being financed like infrastructure. And enterprise AI is being reframed as an operating problem, not a model problem.
Where, specifically, would an AI system acting on your behalf create the most value, and what is the one control (permissioning, audit, rollback, verification) you do not yet have to make that safe?
Signal + Noise is strategic intelligence, not engagement-specific advice. For guidance calibrated to your org, start with Advisory.
See exactly how this impacts your specific industry and function. Upgrade to PRO to get bespoke tactical breakdowns generated instantly for your operating model.
Go deeper with the Weekly Signal
This is the daily take. The Weekly goes further — full strategic analysis across 8–10 sections, each with a signal read and operator action items. Source panel included.
Sign up free → then upgrade