
Yesterday's signals, distilled, A look back at October 24, 2026.
OpenAI cut frontier training off from the live internet. The UK put £100 million behind an AI Biosecurity Lab with OpenAI, Anthropic, and Google DeepMind. AWS leadership said 2027 capacity is “largely sold out,” with a “good chunk” of 2028 also sold.
In parallel, Japan’s GMO Internet asked the government to use new active cyber defense powers after a hack. And a Business Insider report described “ghost” AI data center projects inflating the apparent grid crunch.
These are not disconnected headlines.
They’re the same move expressed at different layers: tighter custody of inputs, tighter custody of infrastructure, tighter custody of incident response. The “elastic” era, elastic data, elastic compute, elastic responsibility, keeps getting replaced by pre-commitments, controlled environments, and state-linked interfaces.
The strategic question for operators is not whether to adopt frontier capability. It’s whether your organization can prove what you used, where it came from, who touched it, and what happens when it breaks.
INFRASTRUCTURE / CLOUD CAPACITY
Compute is becoming a reserved asset, planning cycles are lengthening
AWS capacity for 2027 “largely sold out,” with 2028 also partially committed
Andy Jassy said AWS capacity for 2027 is “largely sold out” and a “good chunk” of 2028 capacity is also sold, while reserving some capacity for on-demand, per The Information.
This is not a pricing story first. It’s a scheduling story.
So What? If you’re building AI products that assume you can scale inference or training on demand, the constraint is shifting from “can we pay” to “can we get allocation.” That changes how roadmaps get financed and how enterprise contracts get written, capacity becomes a deliverable, not an implementation detail. It also increases the value of portability, because the switching cost is no longer just engineering time, it’s losing your place in line.
The Risk: This can be read too literally, “sold out” is not a public capacity ledger, and AWS still holds back on-demand. But even partial truth here is enough to change procurement behavior across the market.
Action:
- Inventory every workload that assumes burst capacity, tag the ones tied to revenue or contractual SLAs.
- Ask your cloud rep for written guidance on 2027–2028 regional availability for your instance families, then plan around the worst-case answer.
- Stand up a portability drill for one critical inference service, prove you can run it in a second region or provider without a quarter-long rewrite.
GOVERNANCE / BIOSECURITY
Bio-risk is being operationalized as national infrastructure, not lab policy
UK commits £100 million to an AI Biosecurity Lab with OpenAI, Anthropic, and Google DeepMind
The UK plans to invest £100 million to create an AI Biosecurity Lab to boost defenses against biological threats, supported by OpenAI, Anthropic, and Google DeepMind, per BBC.
This is a concrete institutional form, budget, mandate, and named frontier partners.
The Bet: Biosecurity becomes the first domain where “frontier model governance” is enforced through shared facilities, shared evaluation, and shared access rules, not just voluntary commitments.
So What? If you operate anywhere near biology, healthcare data, lab automation, synthesis workflows, clinical decision support, expect procurement to start asking for bio-risk controls as a default requirement. Not “do you have a safety policy,” but “what are your gates, what are your logs, what are your escalation paths, and who audits them.” The lab itself matters less than the template it creates: a repeatable pattern for domain-specific AI governance that other countries can copy.
This also changes partnership dynamics. When frontier labs are embedded in national biosecurity architecture, the “who do we call” question shifts, buyers and regulators will increasingly expect a direct interface between your product and a recognized evaluation regime.
The Risk: A lab announcement is not the same as enforcement. The near-term impact may be uneven, stronger for UK-linked procurement and research ecosystems than for global commercial software. But the direction is clear: domain governance is moving from principles to facilities.
Action:
- Map your product’s “bio adjacency”, data types, workflows, customers, and integrations that could be interpreted as dual-use exposure.
- Add a bio-risk review checkpoint to your model/tooling roadmap, document what you will and won’t support in lab-like workflows.
- Prepare an audit packet now, data provenance, access controls, red-team results, and incident response, so you’re not assembling it under deal pressure.

CAPABILITY / TRAINING CUSTODY
Frontier training is moving from “the web” to controlled snapshots and simulated environments
OpenAI cuts live internet from frontier model training, citing “significant risks”
OpenAI said it will no longer train its frontier AI models on the live internet, citing “significant risks,” per TechCrunch.
Separately, reporting described OpenAI building a “giant fake internet” for agents to use and abuse safely, per Gizmodo.
Two moves, one direction: reduce exposure to uncontrolled inputs while still training systems that can operate in internet-like conditions.
So What? For operators, this changes what “freshness” means. If frontier training is on snapshots, then “what does the model know” becomes a function of update cadence and curated corpora, not ambient ingestion. That pushes value toward proprietary data partnerships, licensed datasets, and internal knowledge bases that can be versioned and audited.
It also raises the bar on evaluation. If labs are training agents in simulated internets, enterprise buyers will start asking what your equivalent is, what sandbox you use to test tool use, browsing, transaction flows, and failure modes before you connect an agent to real systems. The expectation won’t be “trust us.” It will be “show us your environment and your logs.”
The Risk: Snapshot training can widen the gap between “model capability” and “real-world reliability” if the simulation diverges from reality. And for many enterprise deployments, the bigger risk remains tool misuse and permissions, not what the base model saw during training.
Action:
- Version your own “web snapshot” dependencies, if you rely on scraped or third-party corpora, document update cadence and provenance this week.
- Build a minimal agent sandbox, fake accounts, fake payment rails, fake customer records, so you can test failure modes without touching production.
- Update your vendor questionnaire, ask model providers how they handle data freshness, snapshot cadence, and simulation-based safety testing.
SECURITY / STATE INTERFACE
Incident response is starting to route through government capabilities
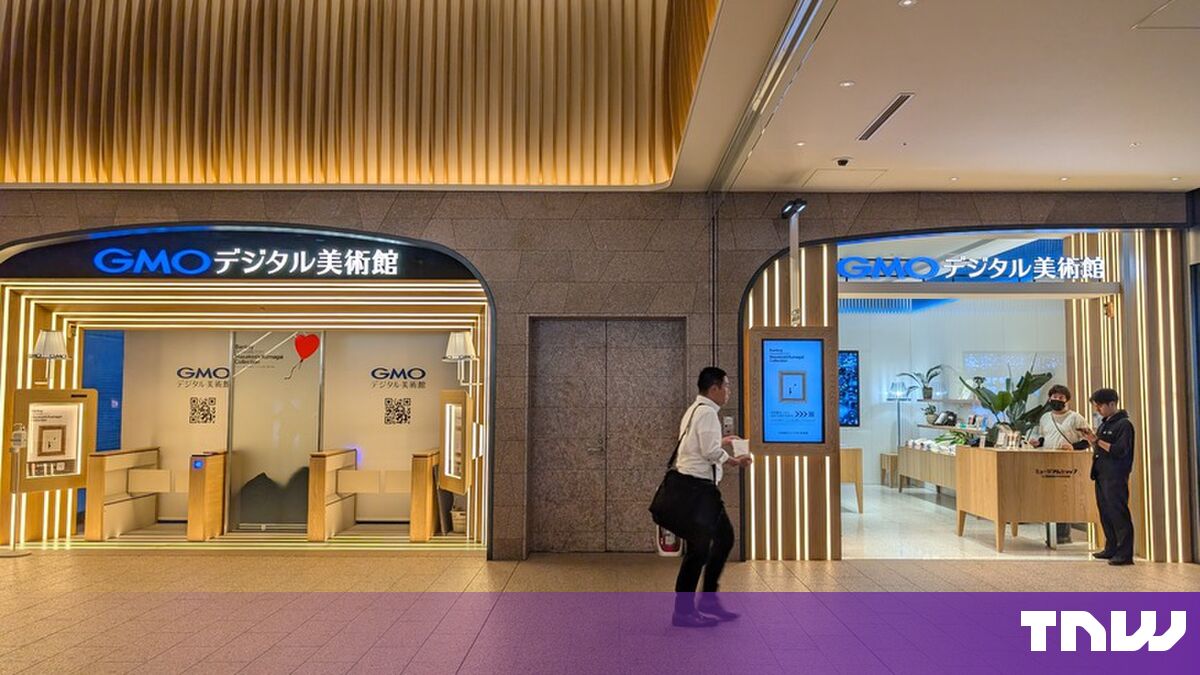
Japan’s GMO Internet requests government cyber defense measures after hack
Japan’s GMO Internet requested government cyber defense measures, per Bloomberg.
The notable part is not that a company got hit. It’s that the company publicly asked the state to engage.
So What? If you operate critical consumer platforms or infrastructure in jurisdictions building “active cyber defense” authority, your breach playbook is no longer just internal plus vendors. It becomes a multi-party governance workflow, legal, regulators, law enforcement, and potentially state cyber units. That changes disclosure timing, evidence handling, and communications strategy.
This also creates a new procurement pressure: boards will ask whether your security program is designed for a world where incidents trigger state involvement. That means cleaner logging, clearer chain-of-custody, and rehearsed interfaces, not improvisation.
The Risk: State involvement can help, but it can also slow decisions, complicate communications, and introduce geopolitical sensitivity, especially for multinationals with cross-border data flows.
Action:
- Add a “state interface” annex to your incident response plan, who calls whom, what gets preserved, what can be shared, and under what authority.
- Run a tabletop exercise that assumes government participation, test comms, legal review, and evidence retention under time pressure.
- Audit your logging retention and access controls, assume you may need to produce defensible timelines and artifacts quickly.
INFRASTRUCTURE / CAPITAL DISCIPLINE (WATCH ITEM)
The grid crunch narrative is getting polluted by speculative queue behavior
Business Insider reported that the AI data center boom has a “ghost problem,” with speculative projects and duplicate power requests inflating perceived demand, per Business Insider.
Signal: The market is starting to separate “announced megawatts” from “financeable megawatts.” Action: Treat MW claims like pipeline, verify interconnect status, power purchase agreements, and permitting before you anchor strategy.
CONTRARIAN SIGNAL
The “safety” story is also a supply-chain story
The surface narrative is governance: biosecurity labs, safer training regimes, simulated internets, state-backed cyber defense.
The underlying mechanism is supply-chain control.
Cutting off live internet training reduces exposure to uncontrolled inputs, yes. It also makes the training pipeline more dependent on curated datasets, licensed sources, and controlled environments. Biosecurity labs create evaluation regimes, yes. They also create chokepoints where access, compliance, and partnership determine who can ship into regulated domains. Cloud capacity being pre-sold is a market dynamic, yes. It also means the ability to reserve compute becomes a competitive capability in its own right.
The takeaway is operational: governance is becoming a gating function on throughput. If you can’t document provenance, simulate safely, and reserve capacity, you don’t just take more risk. You ship slower.
The Takeaway: Treat governance artifacts, provenance, evals, incident interfaces, as throughput infrastructure, not compliance overhead.
THE QUESTION FOR TODAY
Compute is getting reserved years ahead. Training inputs are getting locked down and versioned. Bio-risk is getting institutionalized into national facilities. Incident response is starting to include state capabilities. And infrastructure narratives are getting noisier as capital chases power.
Where, specifically, is your organization still operating on “elastic assumptions”, about data, compute, or responsibility, that will break the next time you try to scale?
Signal + Noise is strategic intelligence, not engagement-specific advice. For guidance calibrated to your org, start with Advisory.
See exactly how this impacts your specific industry and function. Upgrade to PRO to get bespoke tactical breakdowns generated instantly for your operating model.
Go deeper with the Weekly Signal
This is the daily take. The Weekly goes further — full strategic analysis across 8–10 sections, each with a signal read and operator action items. Source panel included.
Sign up free → then upgrade
