
A look at OpenAI's Project Daybreak, which lets vetted partners use its top hacking models to find and fix vulnerabilities and helped uncover PHP2Shell RCE bugs
THE SO WHAT
Offensive-grade LLMs are moving into structured, vetted programs like Project Daybreak—AI red teaming is becoming a formal layer in security posture, not a side experiment. CISOs should start asking vendors how they’re using AI to probe their own surfaces before attackers do.
READ THE SOURCE
MORE FROM THE WIRE
 Applied AI
John Healey pledges to use budget to harness power of AI to bolster Britain’s security
Hundreds of millions in UK budgeted AI spend framed around “security and prosperity” means procurement for defense, border, and critical infrastructure AI is about to thicken. Operators selling into or relying on UK public-sector rails should track how this ‘distinctively British’ AI approach translates into standards, data access rules, and preferred vendors.
 Applied AI
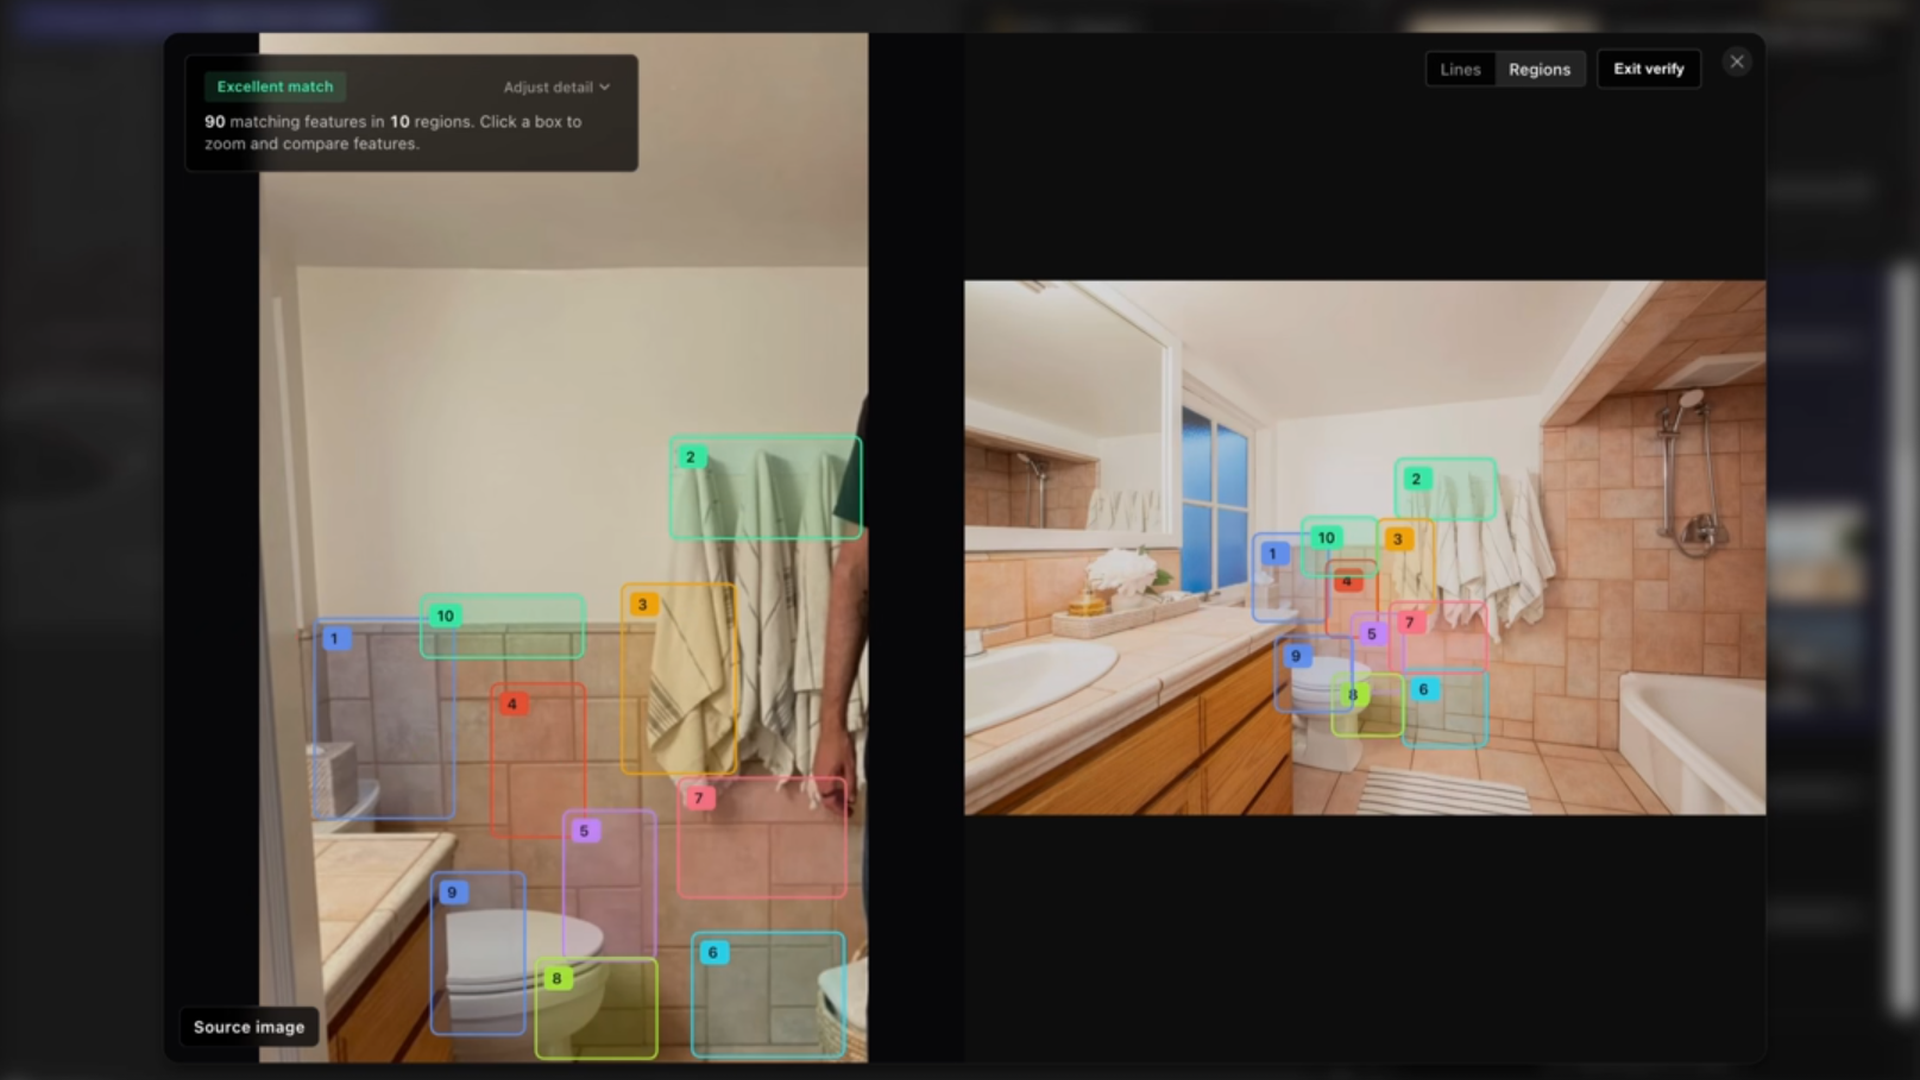
This AI tool can now turn ordinary household photos into location clues — so could law forces use the technology to scope out your home?
If interior photos can be reliably geolocated, every product shot, listing image, and social post becomes latent location data. Map your exposure: marketing, real estate, and marketplace teams need a policy on what gets photographed and how it's stored before this capability becomes commoditized.
 Applied AI
OpenAI says it will no longer train its AI models on the live internet, citing “significant risks”
Cutting frontier models off from the live internet pushes the ecosystem toward curated, slower-moving corpora and proprietary data partnerships. If you’re counting on real-time web grounding as a differentiator, assume more friction, higher licensing costs, and tighter safety scrutiny around whatever you scrape or stream.
Mark Cuban says the best defense against malicious AI agents is more AI
Framing malicious AI agents as “cockroaches” implies an arms race where manual defense is structurally outmatched. CISOs and infra leads should budget for autonomous or semi-autonomous defense systems — detection, triage, and response — rather than assuming human-centric SOC workflows will scale.