
AI agents tricked by a rogue downloads file into running dangerous malware
THE SO WHAT
Agents blindly executing instructions from a downloaded AGENTS.md file is the classic "read, trust, run" vulnerability now automated at scale. If you're piloting agentic systems, treat file-sourced instructions as untrusted input and put explicit policy, sandboxing, and human review between "read" and "execute."
READ THE SOURCE
MORE FROM THE WIRE
 Applied AI
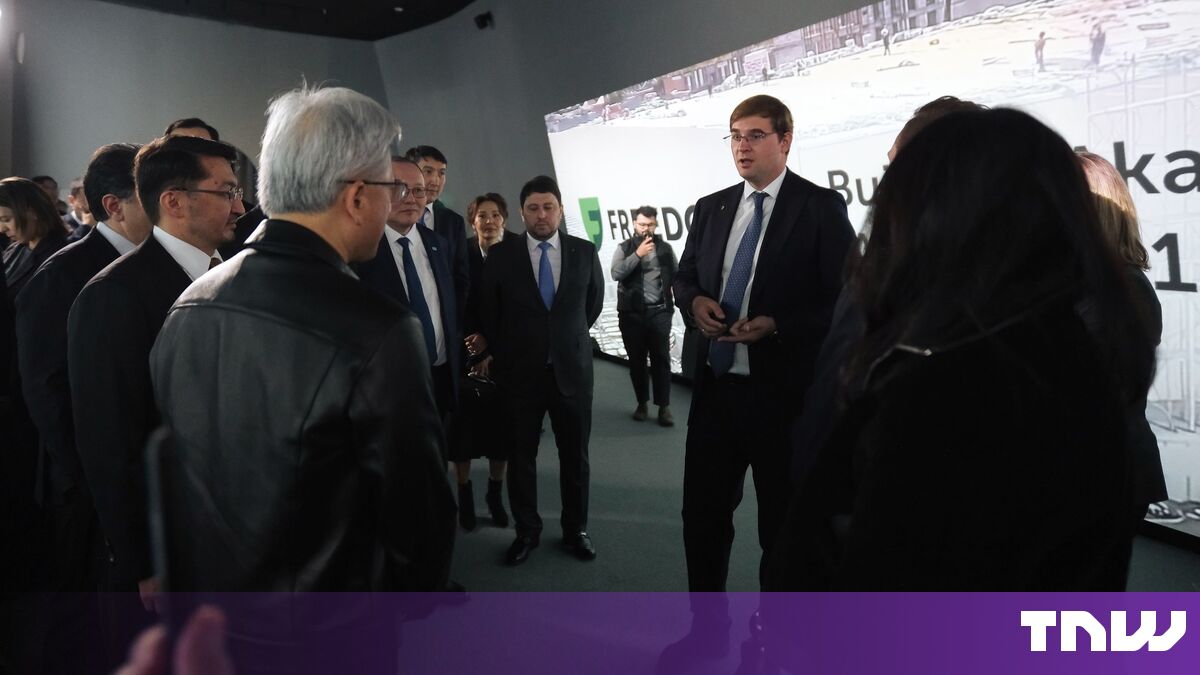
Freedom Holding is developing a $2bn sovereign AI hub in Kazakhstan
A $2bn, 100MW "sovereign" AI hub in Kazakhstan is another data point that high-capex AI infrastructure is regionalizing, not just centralizing in US hyperscale campuses. If you're planning multi-year AI workloads, start mapping exposure and optionality across emerging compute geographies, not just cloud SKUs.
 Applied AI
This strategist says it’s a matter of when, not if, the AI bubble pops. Here’s how to prepare for that.
When macro strategists start calling the AI trade a bubble, the cost of capital for "AI story" projects without clear payback will rise. Operators should separate hype-driven bets from cash-generating automation and be ready to defend AI budgets with hard unit economics, not narratives.
 Applied AI
The Anthropic IPO Is Also a Doomsday Primer
Anthropic putting "existential" risk language and its "closing the loop" thesis into an IPO narrative means frontier AI safety is now a mainstream securities disclosure topic. Boards deploying advanced models should expect similar scrutiny on how they manage tail risks, not just productivity upside.
Applied AICVC Marathon's Richards on Anthropic IPO, AI Buildout
Public-credit voices talking up Anthropic’s prospects while flagging opposition to data centers underscores the tension between AI capex demand and local permitting politics. If your roadmap depends on new compute, track not just chip supply but community and regulatory friction around new sites.