
AI startup hacks Anthropic, gains access to employee details, internal messages
THE SO WHAT
An AI startup reportedly breaching a major lab in 12 hours and pulling employee data and internal messages is a reminder that model builders are now prime targets — and peers may be the adversary. If you run an AI org, treat internal comms, identity systems, and dev tools as crown jewels, not back-office IT.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
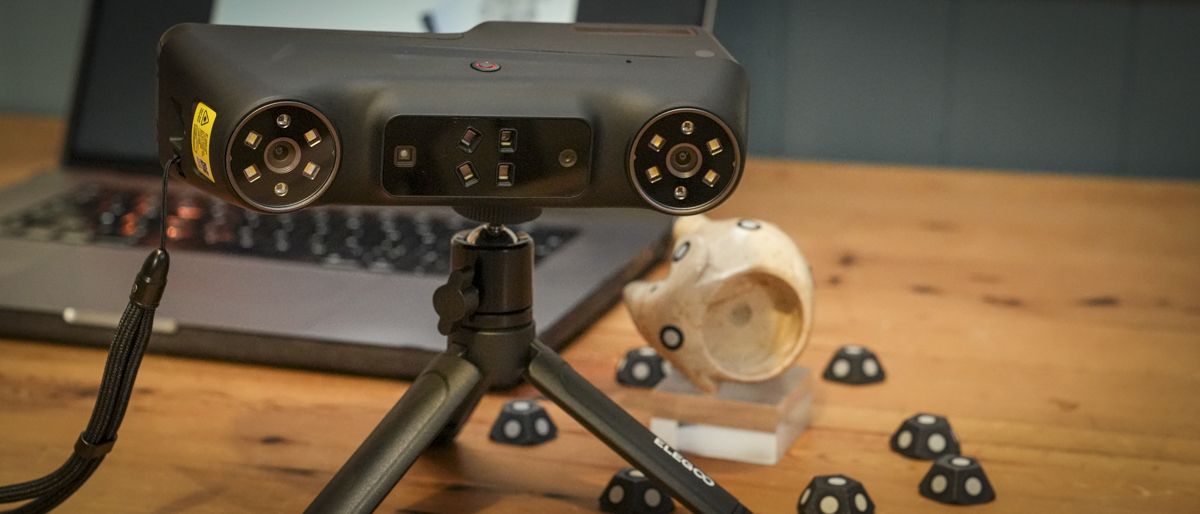
Elegoo M1 Ultra 3D Scanner review
High-accuracy handheld 3D scanning at prosumer pricing pushes more fabrication, repair, and reverse-engineering work in-house. If you run a small shop or product team, this is another nudge to audit which external CAD/scan services you can replace with local capability.
 Deep & Emerging Tech
When Electric Cars Were for Women
The early EV era shows how quickly a technology’s social positioning can flip as infrastructure, performance, and norms change. For climate and mobility builders, it’s a reminder that product framing and cultural narrative are as path-dependent as the tech itself—design for re-segmentation, not a fixed “target user.”
 Deep & Emerging Tech
Nvidia’s Megaspeed ties show potential blind spots in the U.S. effort to block China from accessing advanced chips
Export controls aimed at physical chips leave a large attack surface in cloud access, partnerships, and software-defined performance. If your strategy assumes constrained Chinese access to advanced compute, model your risk with “cloud leakage” as a baseline, not an edge case.
 Deep & Emerging Tech
Spooky New Infostealer Malware Uses AI to ‘Autodox’ Victims
Malware like “Volta-Autodoxer” using AI to correlate credentials, receipts, and sessions into doxxing payloads shows how quickly offense is weaponizing LLMs. Security teams should assume automated OSINT and contextualization at scale—tighten data minimization and monitoring around seemingly low-sensitivity exhaust like food orders and chat logs.