
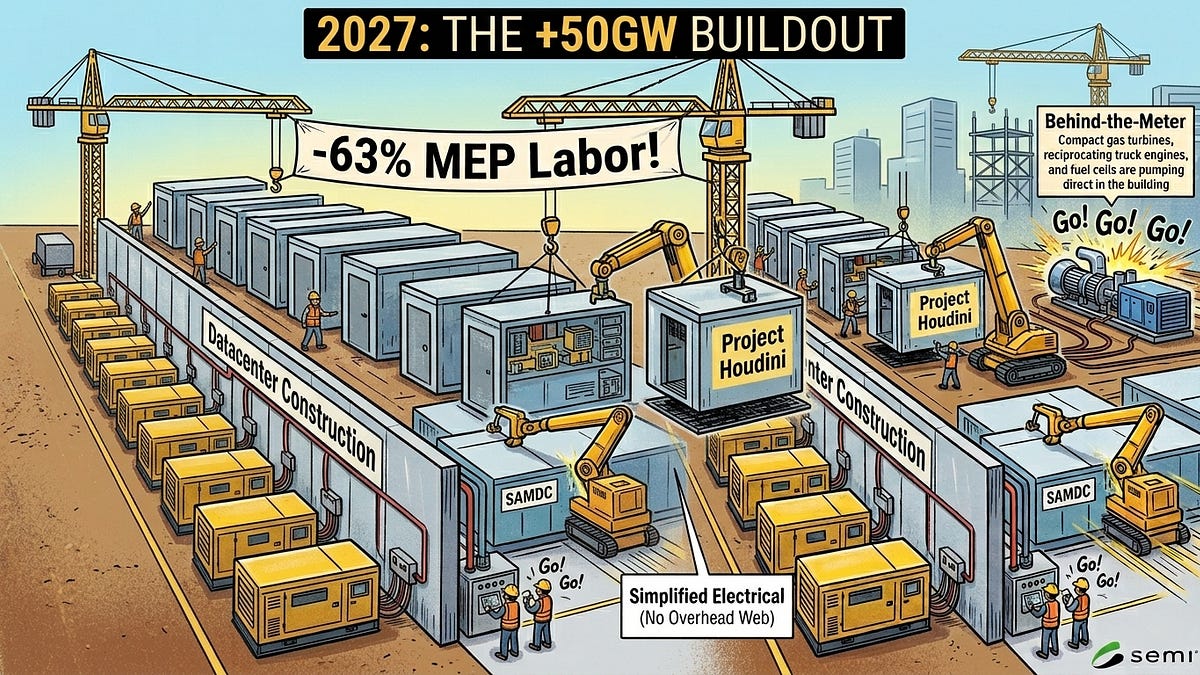
Analysis: companies are set for a massive acceleration of 50GW+ in data center capacity additions in 2027; 24GW+ across 40 campuses are in the advanced stages
THE SO WHAT
A 50GW+ step-up in 2027 with 24GW already in advanced planning means the AI buildout is locked in on a multi-year industrial timeline, not a quarterly hype cycle. If you depend on large-scale compute, your real constraints will be power, land, and interconnect near these 40 campuses—secure those relationships now, not when capacity goes live.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
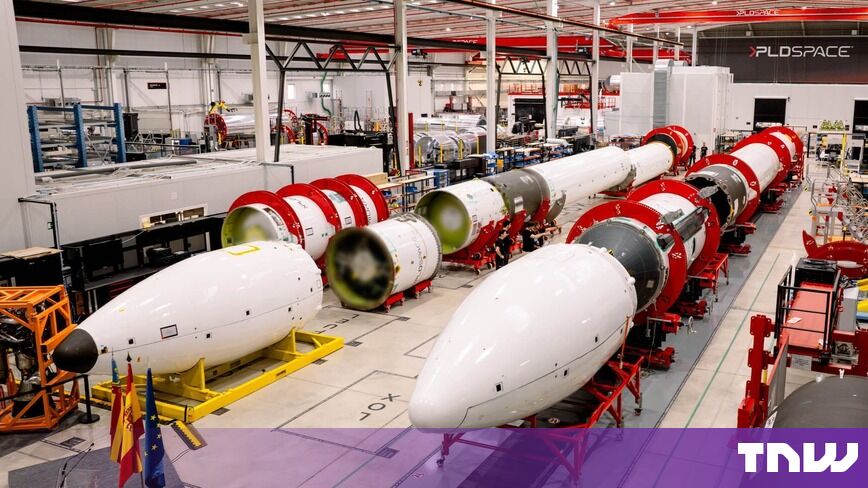
PLD Space starts system-level tests on Miura 5 with three rockets built
Miura 5 entering system-level testing with three vehicles built moves PLD Space from slideware to hardware in the European launch market. If your roadmap depends on smallsat launches, this is another potential provider to price into multi-launch, multi-orbit strategies over the next few years.
 Deep & Emerging Tech
Researcher: a Chinese-speaking hacker used AI agents to target 1,200+ websites and breach 100+ entities, including Deere and SharkNinja, spending ~$5,000 total
One attacker using AI agents to hit 1,200+ sites and breach 100+ entities for roughly $5,000 is the new unit economics of offense. Assume automated recon and exploitation at scale—prioritize hardening basic web assets, credential hygiene, and anomaly detection before you chase exotic threats.
Deep & Emerging TechAmazon and AEP Explore 960-Megawatt Nuclear Project in Indiana
A 960 MW next-gen nuclear project tied to Amazon is a blunt statement: hyperscale AI demand is now reshaping the power mix, not just data center design. If your AI strategy assumes “the cloud will handle it,” start mapping power availability and long-term energy contracts into your capacity planning.
 Deep & Emerging Tech
Whopper of a data breach sees Burger King Japan expose over 11 million customer records
An 11M-record breach at a fast-food app is another reminder that any consumer brand with a loyalty app is effectively a data company with a restaurant attached. If you run high-volume consumer apps, treat auth, encryption, and vendor access as board-level risks, not IT hygiene.