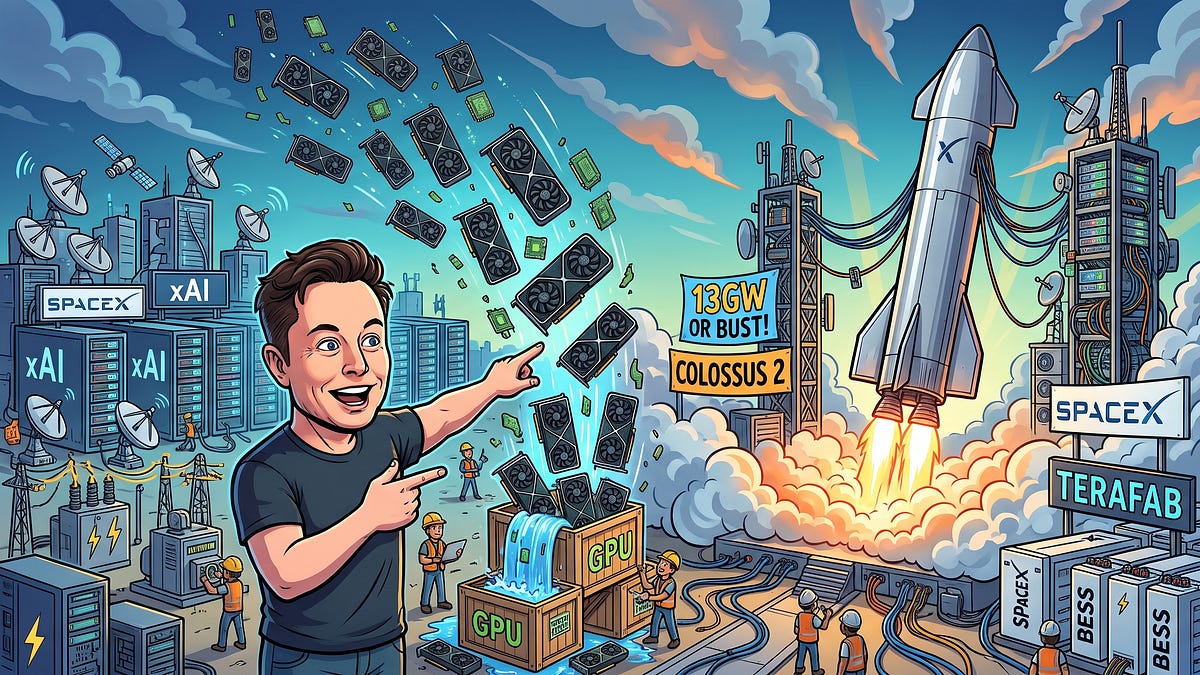
Analysis: SpaceX revises its 2027 data center capacity target up to a record ~13GW, roughly equivalent to all of Google's capacity from 1999-2026 in 1.5 years
THE SO WHAT
Targeting ~13 GW of capacity in 1.5 years is less about one company and more about data centers becoming a heavy-industry game — power, land, and vertically integrated build-out. If you rely on third-party cloud, assume your future bargaining power depends on how many of these vertically integrated players actually deliver.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
French blood banks hacked in latest cyber-attack on Europe
Attackers remotely raising temperatures in French blood cold stores is a reminder that OT and healthcare infrastructure are now live cyber battlefields, not edge cases. If you operate critical environments—labs, warehouses, plants—assume control systems are targets and push for segmented networks and real-time anomaly detection, not just IT-side hardening.
 Deep & Emerging Tech
Most leaked logins are old, but infostealers reach 72% of firms
Infostealers touching 72% of firms with 31.5M exposed credentials means “just rotate passwords” is fantasy—your identity layer is already compromised at scale. Treat endpoint hygiene and phishing training as table stakes and push toward hardware keys, device posture checks, and least-privilege access this budgeting cycle.
 Deep & Emerging Tech
Vauban Seeks More Investments in European District Heating, Fiber, Data Centers
Vauban targeting district heating, fiber, data centers, and batteries as “downturn-resilient” shows infra capital is rotating toward assets that monetize both bits and heat. If you’re planning European compute, expect more sophisticated infra investors at the table—and more scrutiny on your power, cooling, and grid-integration story.
Deep & Emerging TechCyberattackers Drain Money From French Bank Credit Mutuel Arkea
Direct theft from a major bank via compromised systems is a reminder that financial infrastructure is now a live-fire cyber range, not a theoretical risk. If you’re running anything that touches balances or settlement, treat lateral movement and credential abuse as design assumptions, not edge cases.