
Brain Drain Is a Bigger Threat to National Cybersecurity Than AI
THE SO WHAT
Framing brain drain as a larger cybersecurity risk than AI highlights a simple constraint—defense capacity is bottlenecked by human expertise, not just tooling. CISOs and public-sector leaders should treat retention and training of security talent as core infrastructure, on par with buying new platforms.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
Accelerating the search for antimicrobial peptides with Google Antigravity
Using Google Antigravity to accelerate antimicrobial peptide discovery is another data point that generative models are becoming core lab equipment, not side projects. If you run R&D in biotech, the decision isn’t whether to use these tools—it’s which assays, IP boundaries, and validation loops you’re willing to plug into model-driven search.
 Deep & Emerging Tech
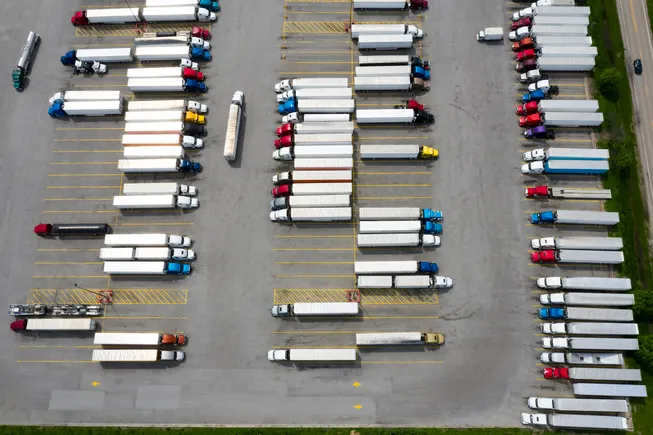
$200M in federal funds to aid truck parking in 12 states
A $200M federal push for truck parking is a hard infrastructure bet that also creates new surfaces for telematics, safety, and eventually autonomy staging. If you build logistics tech, treat these new lots as future sensor and data nodes—design your products to plug into parking availability, security, and driver services from day one.
 Deep & Emerging Tech
Sweden Joins European Quantum and AI Skills Academies
Sweden joining the pan-European Quantum and AI Skills Academies is another move to centralize talent development as quantum tech leaves the lab. If you’re hiring in Europe for deep tech, expect more structured pipelines from these academies—and more competition from national programs for the same graduates.
 Deep & Emerging Tech
'What appears to be a simple scam message is often the visible end of a much larger transnational cybercriminal operation': Microsoft leads global takedown of phishing network which sent over a billion messages
A phishing network sending over a billion messages and tied to a sprawling underground account market shows how industrialized low-skill cybercrime has become. Security teams should treat “commodity” phishing as a supply-chain problem—map where your identity, email, and payment providers intersect with these markets, not just train users to spot bad links.