
CISA confirms attackers are exploiting both PHP2Shell flaws
THE SO WHAT
PHP2Shell landing in CISA’s KEV list with a 48-hour federal patch deadline is a clear signal that web app plumbing remains a live-fire zone. If you have any PHP exposure—direct or via vendors—treat this as a forced inventory moment and tighten your SLA for patching internet-facing components.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
China Is So Desperate for AI Memory That It’s Producing Chips With a 70% Failure Rate
A 70% failure rate on advanced DRAM is a price China is willing to pay to claw back AI memory supply—yield pain is being traded for geopolitical independence. If you rely on high-bandwidth memory, treat supply as structurally constrained and model scenarios where Chinese demand is met domestically instead of on global markets.
 Deep & Emerging Tech
NVision and HyperLight Partner to Develop Photonic Quantum Chips
Pairing molecular qubits with thin-film lithium niobate photonics is a bet that quantum networking and compute will converge at the chip level. If your roadmap assumes classical-only acceleration, start a watchlist on photonic quantum vendors—interface standards and integration points will be the first places this hits you.
 Deep & Emerging Tech
Micron’s stock rises after SK Hynix earnings. Here’s its next major test.
Memory is re-rating as an AI proxy trade—SK Hynix earnings lifting Micron ahead of Samsung’s print shows how tightly investor sentiment is tied to AI demand curves. For operators, that volatility flows through to capex planning: lock in key memory supply and pricing where you can, or build more elasticity into deployment timelines.
 Deep & Emerging Tech
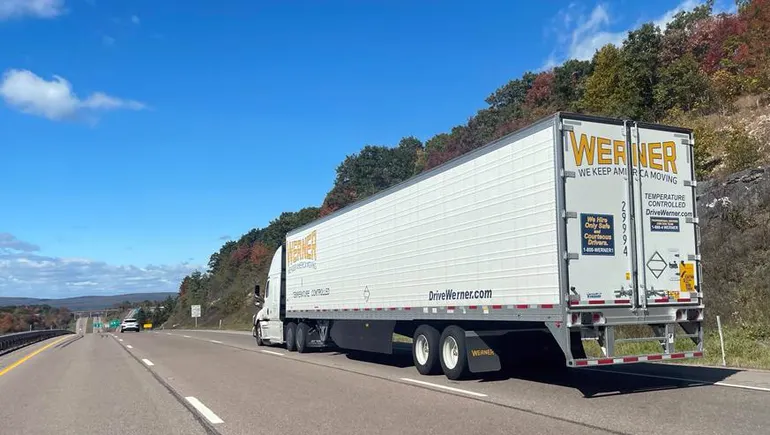
Werner revenue jumps 23% as fleet efficiency improves
A 23% revenue jump tied to fleet efficiency is a concrete example of how optimization—routing, loading, utilization—moves the P&L in logistics. If you operate physical networks, your AI priority should be boring: instrument assets, clean the data, and let optimization models compound margin before you chase flashier use cases.