
CISA warns hackers are exploiting max severity GitLab flaw — urges all businesses to patch immediately
THE SO WHAT
A 10/10 GitLab vuln on CISA’s KEV list with a three-day patch deadline means this is active, not theoretical — CI/CD and code-hosting are now prime targets. If you run GitLab anywhere in your stack, treat this like a production outage: patch, verify exposure, and log access to repos that could have been scraped.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
New York Seizes a Dozen Celebrity Deepfake Websites
New York seizing 12 deepfake sites targeting ~1,200 victims is a clear move to criminalize the infrastructure behind synthetic abuse, not just individual actors. If your platform touches user-generated media, assume prosecutors will expect proactive detection and takedown of deepfakes, not just reactive moderation.
 Deep & Emerging Tech
Digital rights advocates urge EU to step in and save encryption from Canada's Bill C-22
Pushback on Canada’s Bill C-22 from global digital rights groups — and calls for EU intervention — show that national moves against end-to-end encryption have cross-border consequences. If your product depends on strong encryption, track this as a potential precedent that could force architectural changes or regional feature flags.
 Deep & Emerging Tech
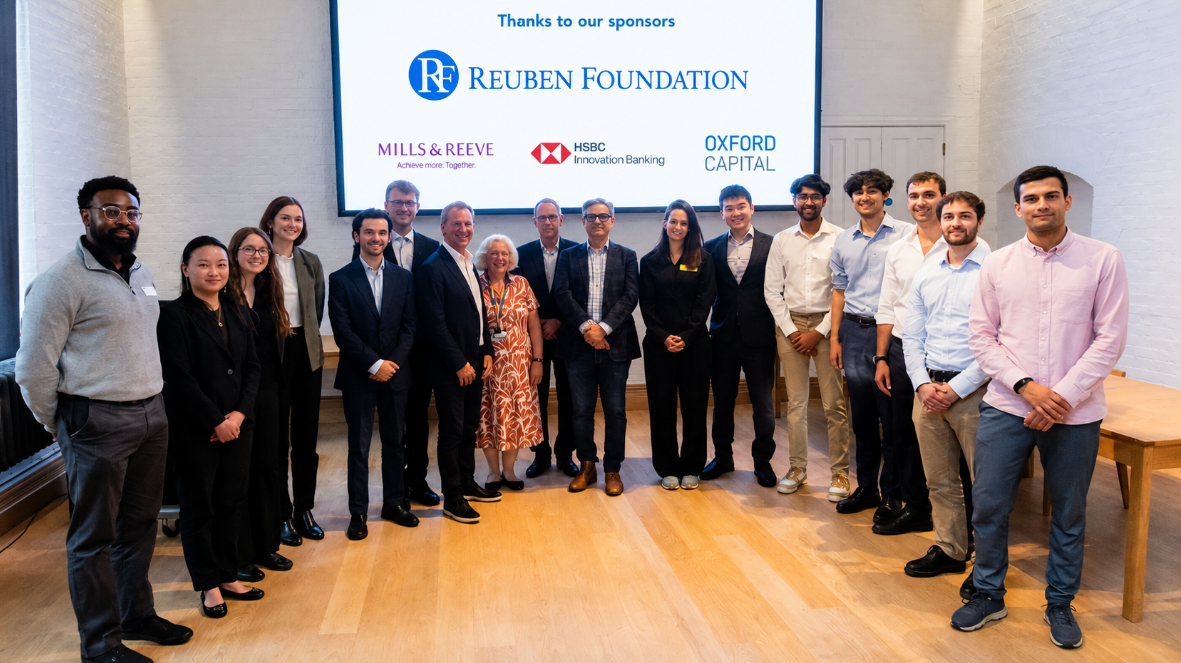
Oxford Quantum Startup Cloq Wins Top Prize at Reuben Entrepreneurship Forum
Another quantum startup winning university pitch forums shows how much early talent and capital are clustering around quantum software and control layers. If you’re in adjacent infra — cryo, control electronics, error correction, compilers — now is the time to map where these teams might become downstream customers or partners.
 Deep & Emerging Tech
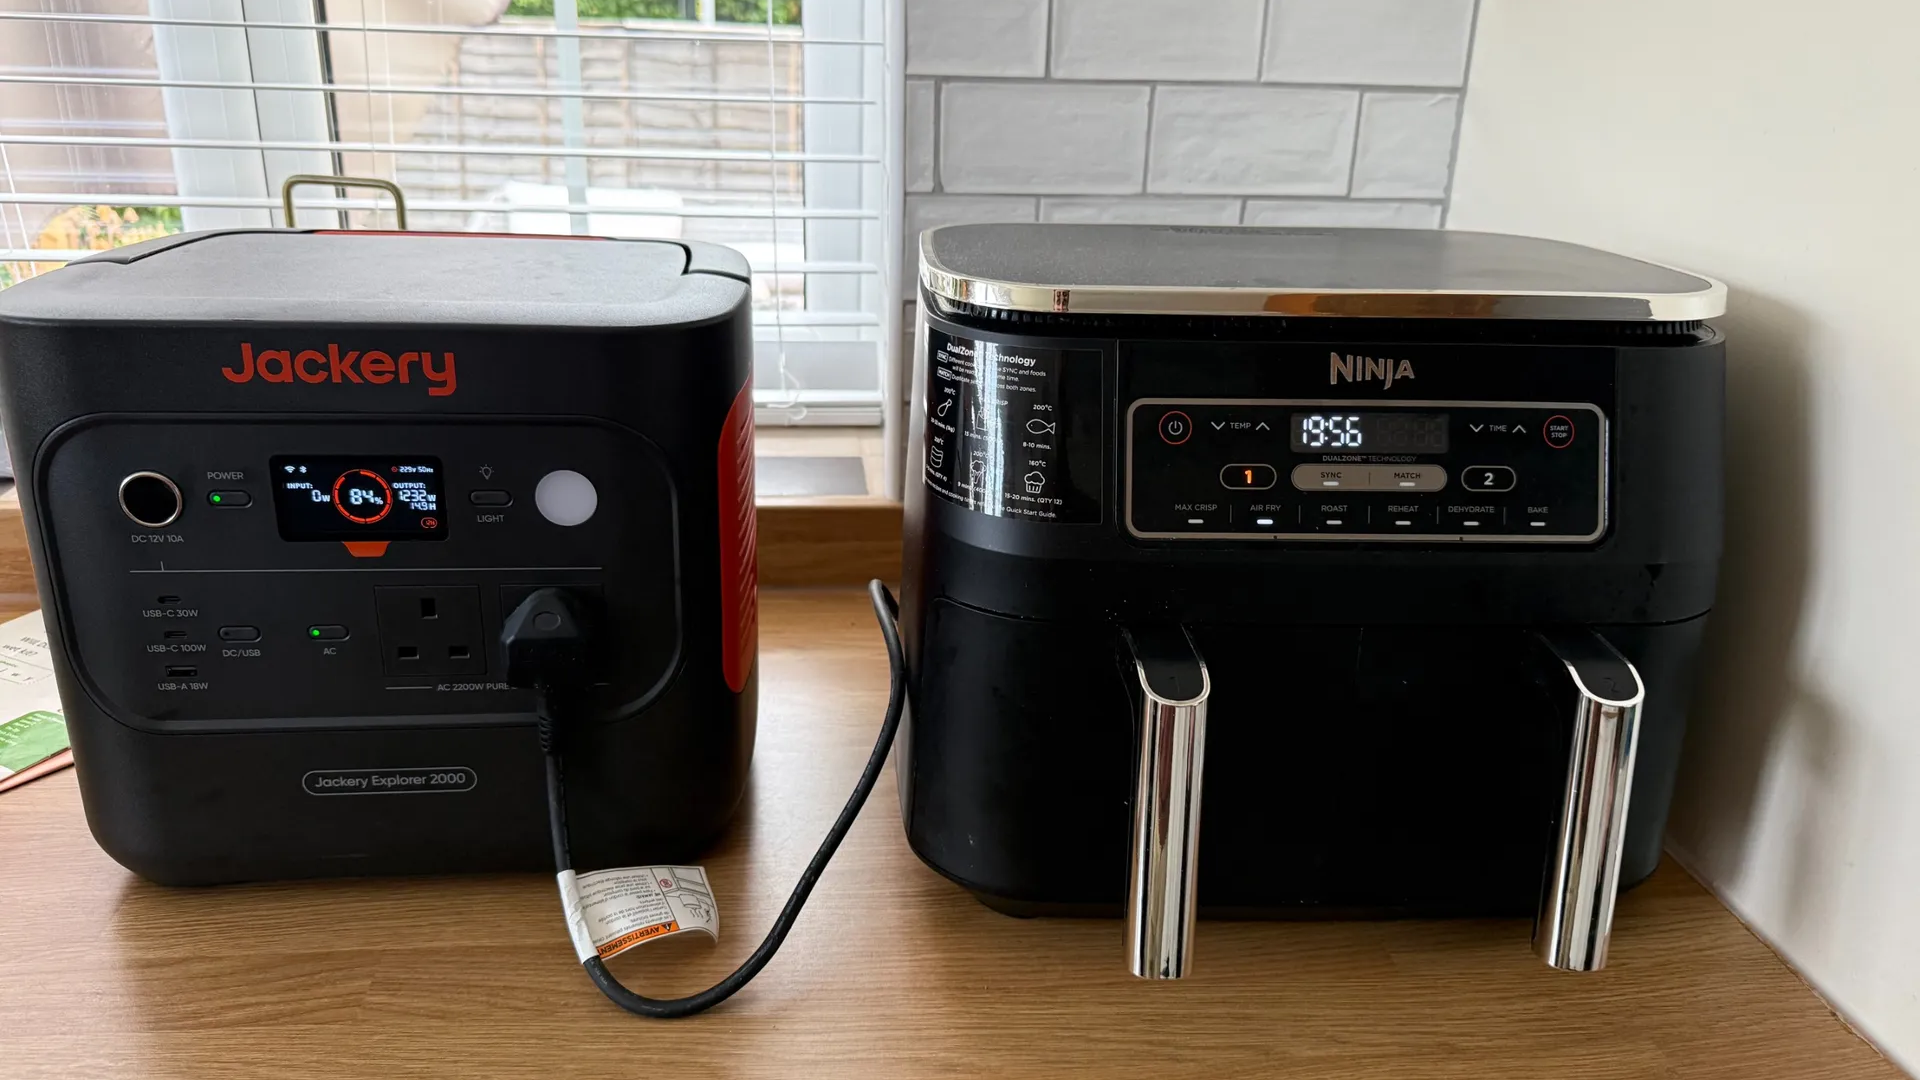
Dinner time saved and toddler meltdown avoided – my experience with the Jackery Explorer 2000 v2 power station
A consumer story about a Jackery 2000 v2 keeping a household running is a microcosm of a bigger pattern — portable storage is becoming mainstream resilience infrastructure. If your product or service is power-sensitive, assume more customers will have local backup and design experiences that degrade gracefully rather than just fail.