

GitLab patches a critical flaw that lets unauthenticated attackers run code on self-managed servers, affecting every release since 7.0 in 2014
THE SO WHAT
A CVSS 10.0 RCE in every self-managed GitLab release since 2014 is a supply-chain blast radius event—your CI/CD is now a primary attack surface. If you host GitLab, patch immediately and assume compromise until proven otherwise, then revisit how you segment and monitor build infrastructure.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
Why is everyone talking about PHP’s ‘critical’ security flaws?
Legacy runtimes like PHP quietly underpin huge swaths of the web — when they surface with ‘critical’ flaws, you’re seeing the accumulated security debt of the last 20+ years. If you run WordPress or PHP apps, treat this as a trigger to inventory exposure and tighten patch SLAs, not just a one-off CVE response.
 Deep & Emerging Tech
Data centers could erase decades of air quality gains
If Texas data center growth can erase 20 years of air quality gains, AI buildout is now a public health and permitting issue, not just an energy and land-use problem. Sensitive: true
 Deep & Emerging Tech
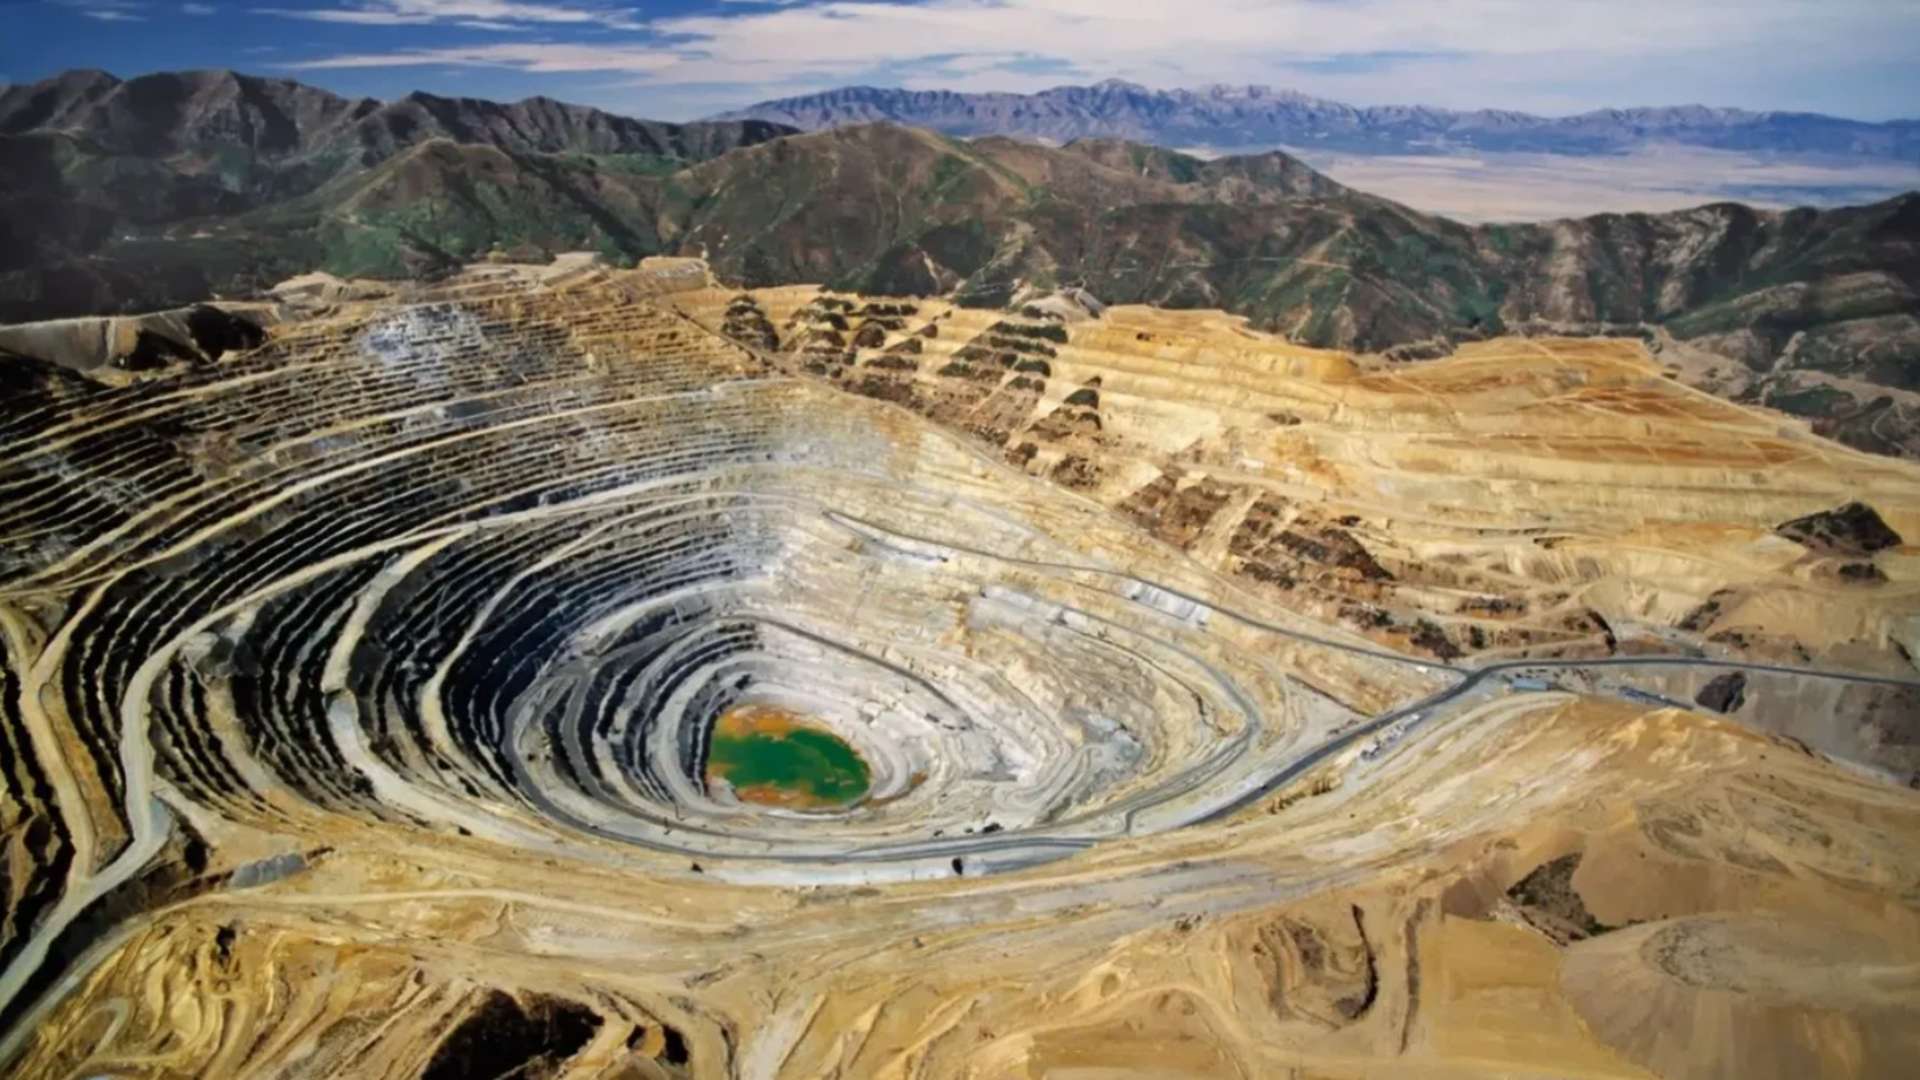
'Data centers can be located in exhausted open pits': Russia eyes 300-meter-deep coal mines to shield server infrastructure from Ukrainian drones
Designing data centers 300 meters underground to avoid drones and leverage passive cooling shows how compute is now treated as strategic infrastructure in conflict zones. If your footprint is even indirectly exposed to geopolitical risk, physical hardening and location strategy belong in the same conversation as chips and power.
 Deep & Emerging Tech
New $4.2 Billion Texas Gas Pipe to Supply Fuel for Data Center
A $4.2B dedicated gas pipeline for a single data center complex makes AI compute an upstream energy customer, not just a cloud workload. If you’re planning large-scale AI deployments, treat fuel mix, grid interconnects, and long-term energy contracts as first-order constraints, not facilities afterthoughts.