

Hackers Exploited the PHP Vulnerabilities Days Before They Were Patched
THE SO WHAT
Zero-days in core web stacks are now being weaponized at cloud scale before most teams even see the CVE. If you’re still treating PHP and similar runtimes as “legacy but stable,” move them into your active threat model and tighten your patch-to-deploy loop.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
Elon Musk Claims His Terafab Will Produce Its First Chip By Mid-2027
A mid-2027 tape-out target for a new fab is an aggressive bet that AI-era chip demand justifies compressing traditional semiconductor timelines. For operators, the takeaway isn’t the date—it’s that more players are willing to treat advanced fabs as strategic assets, not just vendor capacity.
 Deep & Emerging Tech
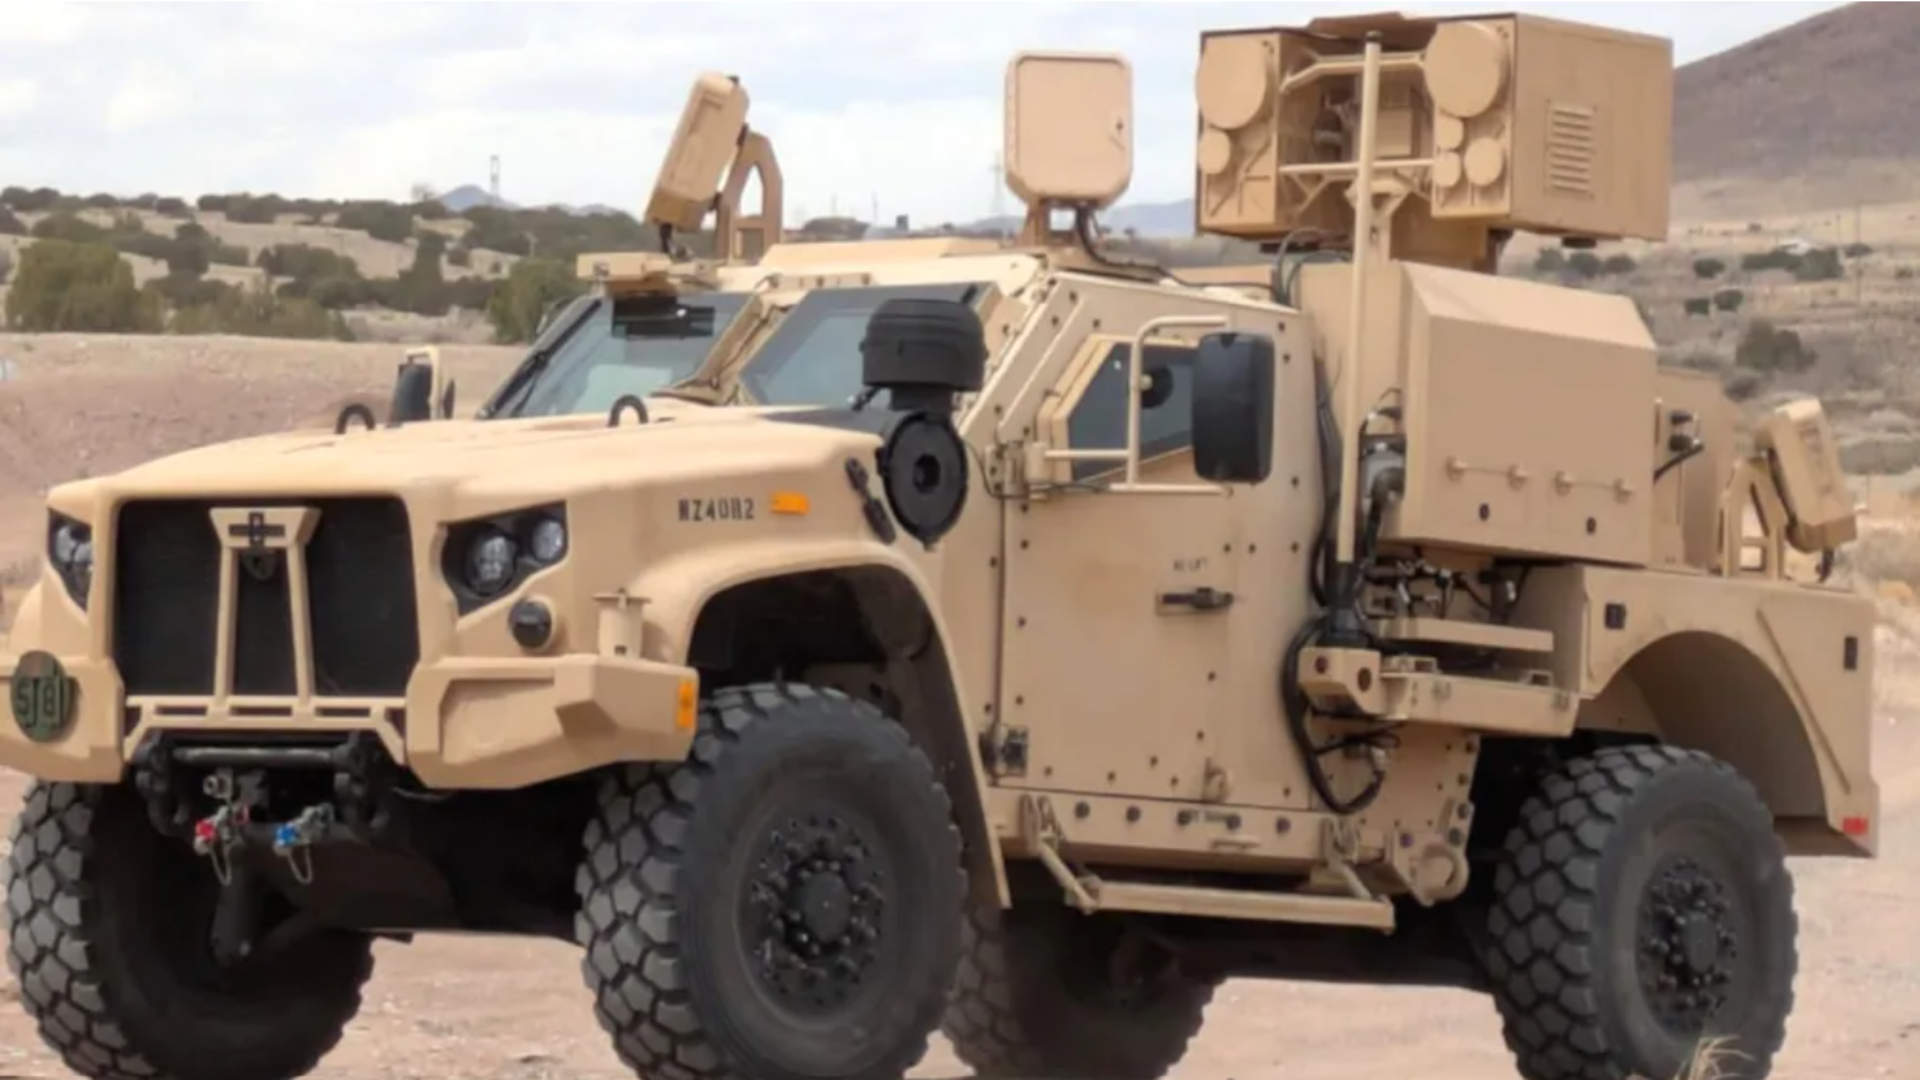
US Army moves away from dedicated laser vehicles — modular LOCUST X3 laser turns standard army trucks into speed-of-light counter-drone rigs for $5 a shot
The Army shifting to modular LOCUST X3 lasers on standard trucks is a bet that counter-drone will be a software-and-power problem, not a bespoke-vehicle problem. For any organization facing cheap, proliferating aerial threats, the pattern is clear — flexible mounts and interchangeable payloads beat specialized platforms.
 Deep & Emerging Tech
Why is everyone talking about PHP’s ‘critical’ security flaws?
Legacy runtimes like PHP quietly underpin huge swaths of the web — when they surface with ‘critical’ flaws, you’re seeing the accumulated security debt of the last 20+ years. If you run WordPress or PHP apps, treat this as a trigger to inventory exposure and tighten patch SLAs, not just a one-off CVE response.
 Deep & Emerging Tech
Data centers could erase decades of air quality gains
If Texas data center growth can erase 20 years of air quality gains, AI buildout is now a public health and permitting issue, not just an energy and land-use problem. Sensitive: true