
Hackers Morph Exposed AI Models Into Tools for Cybercrime
THE SO WHAT
Open models with weak or absent deployment guardrails are now an offensive asset, not just a research curiosity. If you're shipping models or APIs, treat safety as a runtime control problem — lock down weights, add abuse monitoring, and assume adversarial fine-tuning is in play.
READ THE SOURCE
MORE FROM THE WIRE
 Applied AI
Bill Gates says to prepare for 20 years of ‘tumultuous’ AI disruption
A 20-year disruption frame from Gates is a cue to stop treating AI as a 2–3 year tooling refresh and start aligning capex, talent, and policy bets on a generational horizon. For operators, that means pairing aggressive near-term automation pilots with a written thesis on where your moat shifts over a decade, not just a budget cycle.
 Applied AI
I needed 20+ years of address history. Gemini found it for me in minutes
This is the real consumer wedge for assistants—digging structured answers out of your own unstructured data faster than you can. For internal tools, the parallel is obvious: wire AI into your document stores for specific, high-friction workflows like compliance forms and onboarding, not vague “knowledge search.”
 Applied AI
Claude Duet app is Anthropic’s bet on agents
A dedicated Duet app for Pro and Max users is another move to normalize persistent, multi-step agents as a primary interface, not a feature. If your product roadmap still assumes single-shot chat, you’re underestimating how quickly users will expect background execution and task memory.
 Applied AI
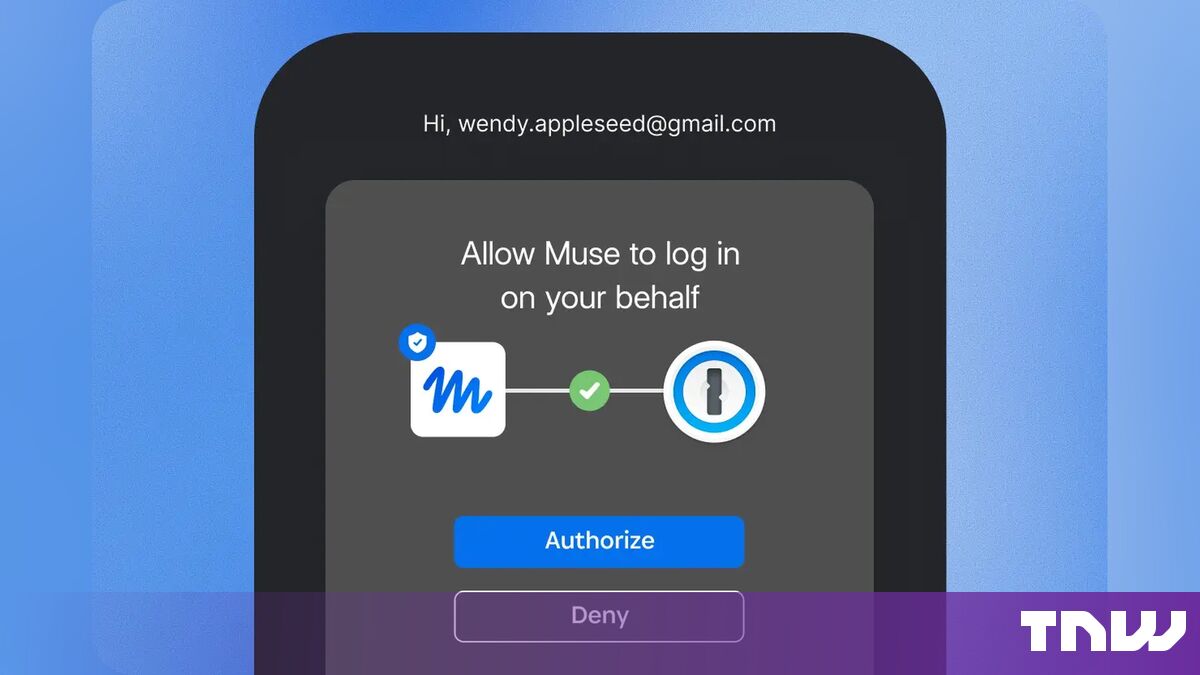
1Password lets AI agents sign in for users without seeing their passwords
Letting agents from Meta, OpenAI, Anthropic, and others authenticate without ever seeing passwords formalizes a new trust boundary—your password manager becomes the broker between humans, agents, and apps. If you’re building agents, assume you’ll need to integrate with these brokers rather than rolling your own credential handling, both for security and enterprise acceptance.