

In open source cybersecurity, AI is kind of a problem — but it can also be a solution
THE SO WHAT
With ~66,000 new vulnerabilities expected in 2026—many AI-generated—defenders are facing an attack surface humans alone can't track. Security teams should be piloting AI for triage, correlation, and patch prioritization, while tightening controls on AI-generated code entering production.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
izmo Microsystems and IIT Madras Advance ₹99.94 Crore Silicon Photonics Program
A nearly ₹100 crore Phase II silicon photonics program in India is another data point that advanced packaging and photonics are going multipolar. Chip and systems teams should start mapping non-US, non-Taiwan supply options for high-bandwidth interconnects into their 3–5 year roadmaps.
 Deep & Emerging Tech
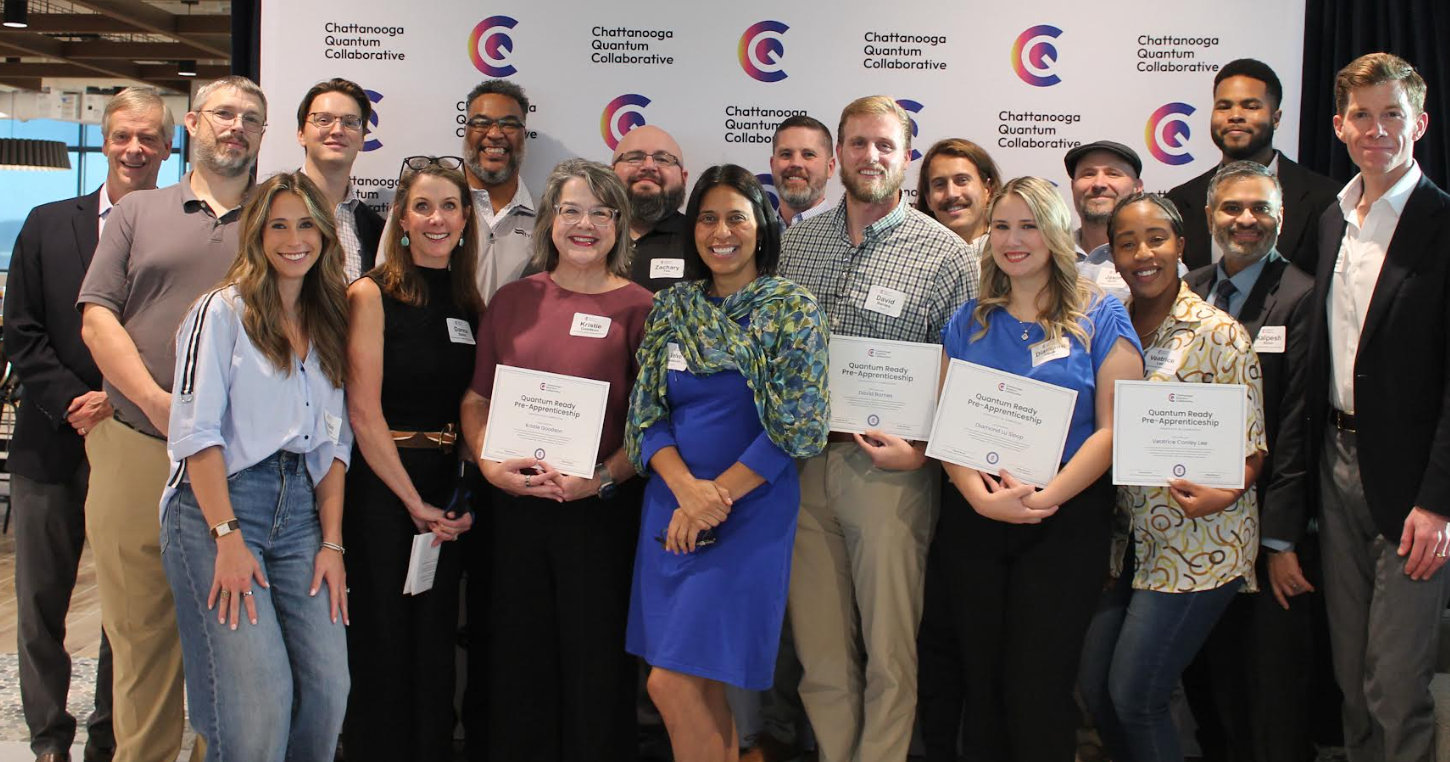
Chattanooga Quantum Collaborative Graduates First Quantum Ready Cohort
A regional "Quantum Ready" pre-apprenticeship graduating 17 professionals is tiny in headcount but important as a template—quantum talent pipelines are starting to look like trade programs, not just PhDs. If quantum touches your 5–10 year plan, engage with these local initiatives now to shape the skills you’ll be hiring.
 Deep & Emerging Tech
Xona’s commercial GPS alternative is about to go live
A commercial GPS alternative entering beta with six dedicated satellites is a strategic shift—navigation and timing are no longer purely government infrastructure. Any operator with autonomy, drones, or time-sensitive trading in their stack should evaluate multi-constellation support and how quickly they could pivot to a private service like Xona.
 Deep & Emerging Tech
The Chinese developer of ARTEX says it has converted the AI agent into a closed-source project after CrowdStrike said it was used to hack South Korean banks
An AI agent allegedly used in Korean bank hacks going closed-source is a reminder that dual-use AI tools are now part of the offensive security stack. If you ship agents or automation frameworks, assume they will be repurposed and start building abuse monitoring and kill-switches into your design.