
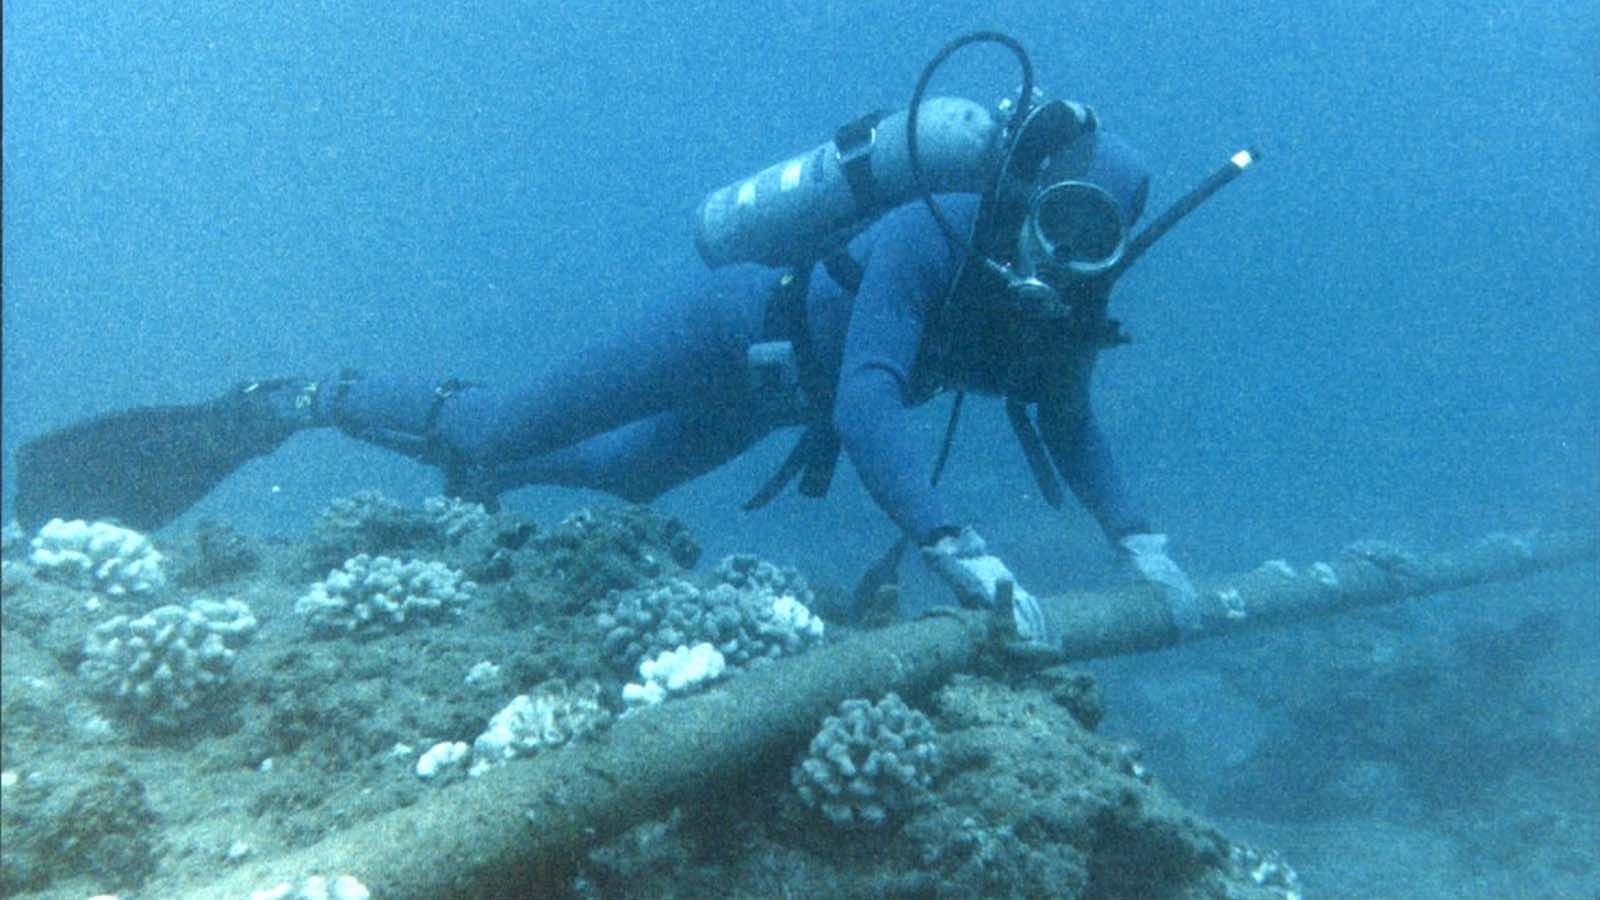
Russian boats spotted loitering over undersea cables connecting Europe and US
THE SO WHAT
Deliberate mapping of undersea cables—500+ incidents in under five years—turns global internet and cloud connectivity into a visible geopolitical attack surface. If your operations depend on transatlantic latency or bandwidth, treat cable disruption as a scenario to model, not a black-swan edge case.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
From Blackouts to Surplus: How Eskom Turned South Africa’s Power Around
Eskom swinging from rolling blackouts to a 3–5 GW surplus while cities still suffer local outages shows the gap between generation and last-mile reliability. If you’re siting compute or manufacturing in South Africa, diligence needs to go down to municipal grid and substation resilience—not just national capacity numbers.
Deep & Emerging TechChina's Star 50 index of AI and chip leaders is down by 40% in under four months, losing ~$480B in market value; chipmaker CXMT is down ~25% in the past month
A 40% drawdown and ~$480B vaporized in China’s AI/chip names is a reminder that public markets will reprice hype long before fundamentals catch up. For operators, this means Chinese vendors may become more aggressive on pricing and partnerships, while global investors get more selective about which AI infra stories they underwrite.
 Deep & Emerging Tech
Microsoft ships emergency .NET fixes for a critical Brotli flaw
A buffer overflow in a ubiquitous compression library—surfaced by an AI lab’s security team—shows how deeply shared components like Brotli sit in your blast radius. Treat this as a dry run: inventory where Brotli and similar third-party libraries live in your stack and tighten your patch and SBOM processes now, not after the next CVE.
 Deep & Emerging Tech
A 16-year-old bug could be putting millions of routers at risk — despite Broadcom saying it patched the issue years ago
A Wi‑Fi flaw “fixed” at the chip vendor but never propagated into millions of routers is a supply-chain governance problem, not just a CVE. If you ship or depend on embedded devices, you need explicit ownership for tracking upstream fixes and pushing firmware updates—otherwise your edge is quietly accumulating 16‑year‑old liabilities.