
Security researchers in an OpenAI bug bounty program hacked OpenAI, accessing its "monorepo" on GitHub, using a cybersecurity version of Opus 4.8 and Opus 5
THE SO WHAT
Offense is now using frontier models as first-class tools—model-assisted red teaming just jumped from theory to production. If you run anything sensitive, assume attackers have comparable AI assistance and upgrade your own security stack and bug bounty scope accordingly.
READ THE SOURCE
MORE FROM THE WIRE
Anthropic says Claude is now leading more than a quarter of its AI research
If Claude is driving 26% of Anthropic’s own AI research, vendor dogfooding has crossed into core R&D—not just productivity demos. Enterprise teams should be mapping which internal knowledge work could follow the same pattern and where governance or IP risk makes that a non-starter.
 Applied AI
Pessimism Reigns Over AI and Jobs, Pew Poll Finds
If 46% of people across 37 countries expect AI to kill more jobs than it creates, you’re going to face political and internal resistance on every automation move. Treat comms, retraining, and role redesign as part of the deployment budget, not an afterthought.
 Applied AI
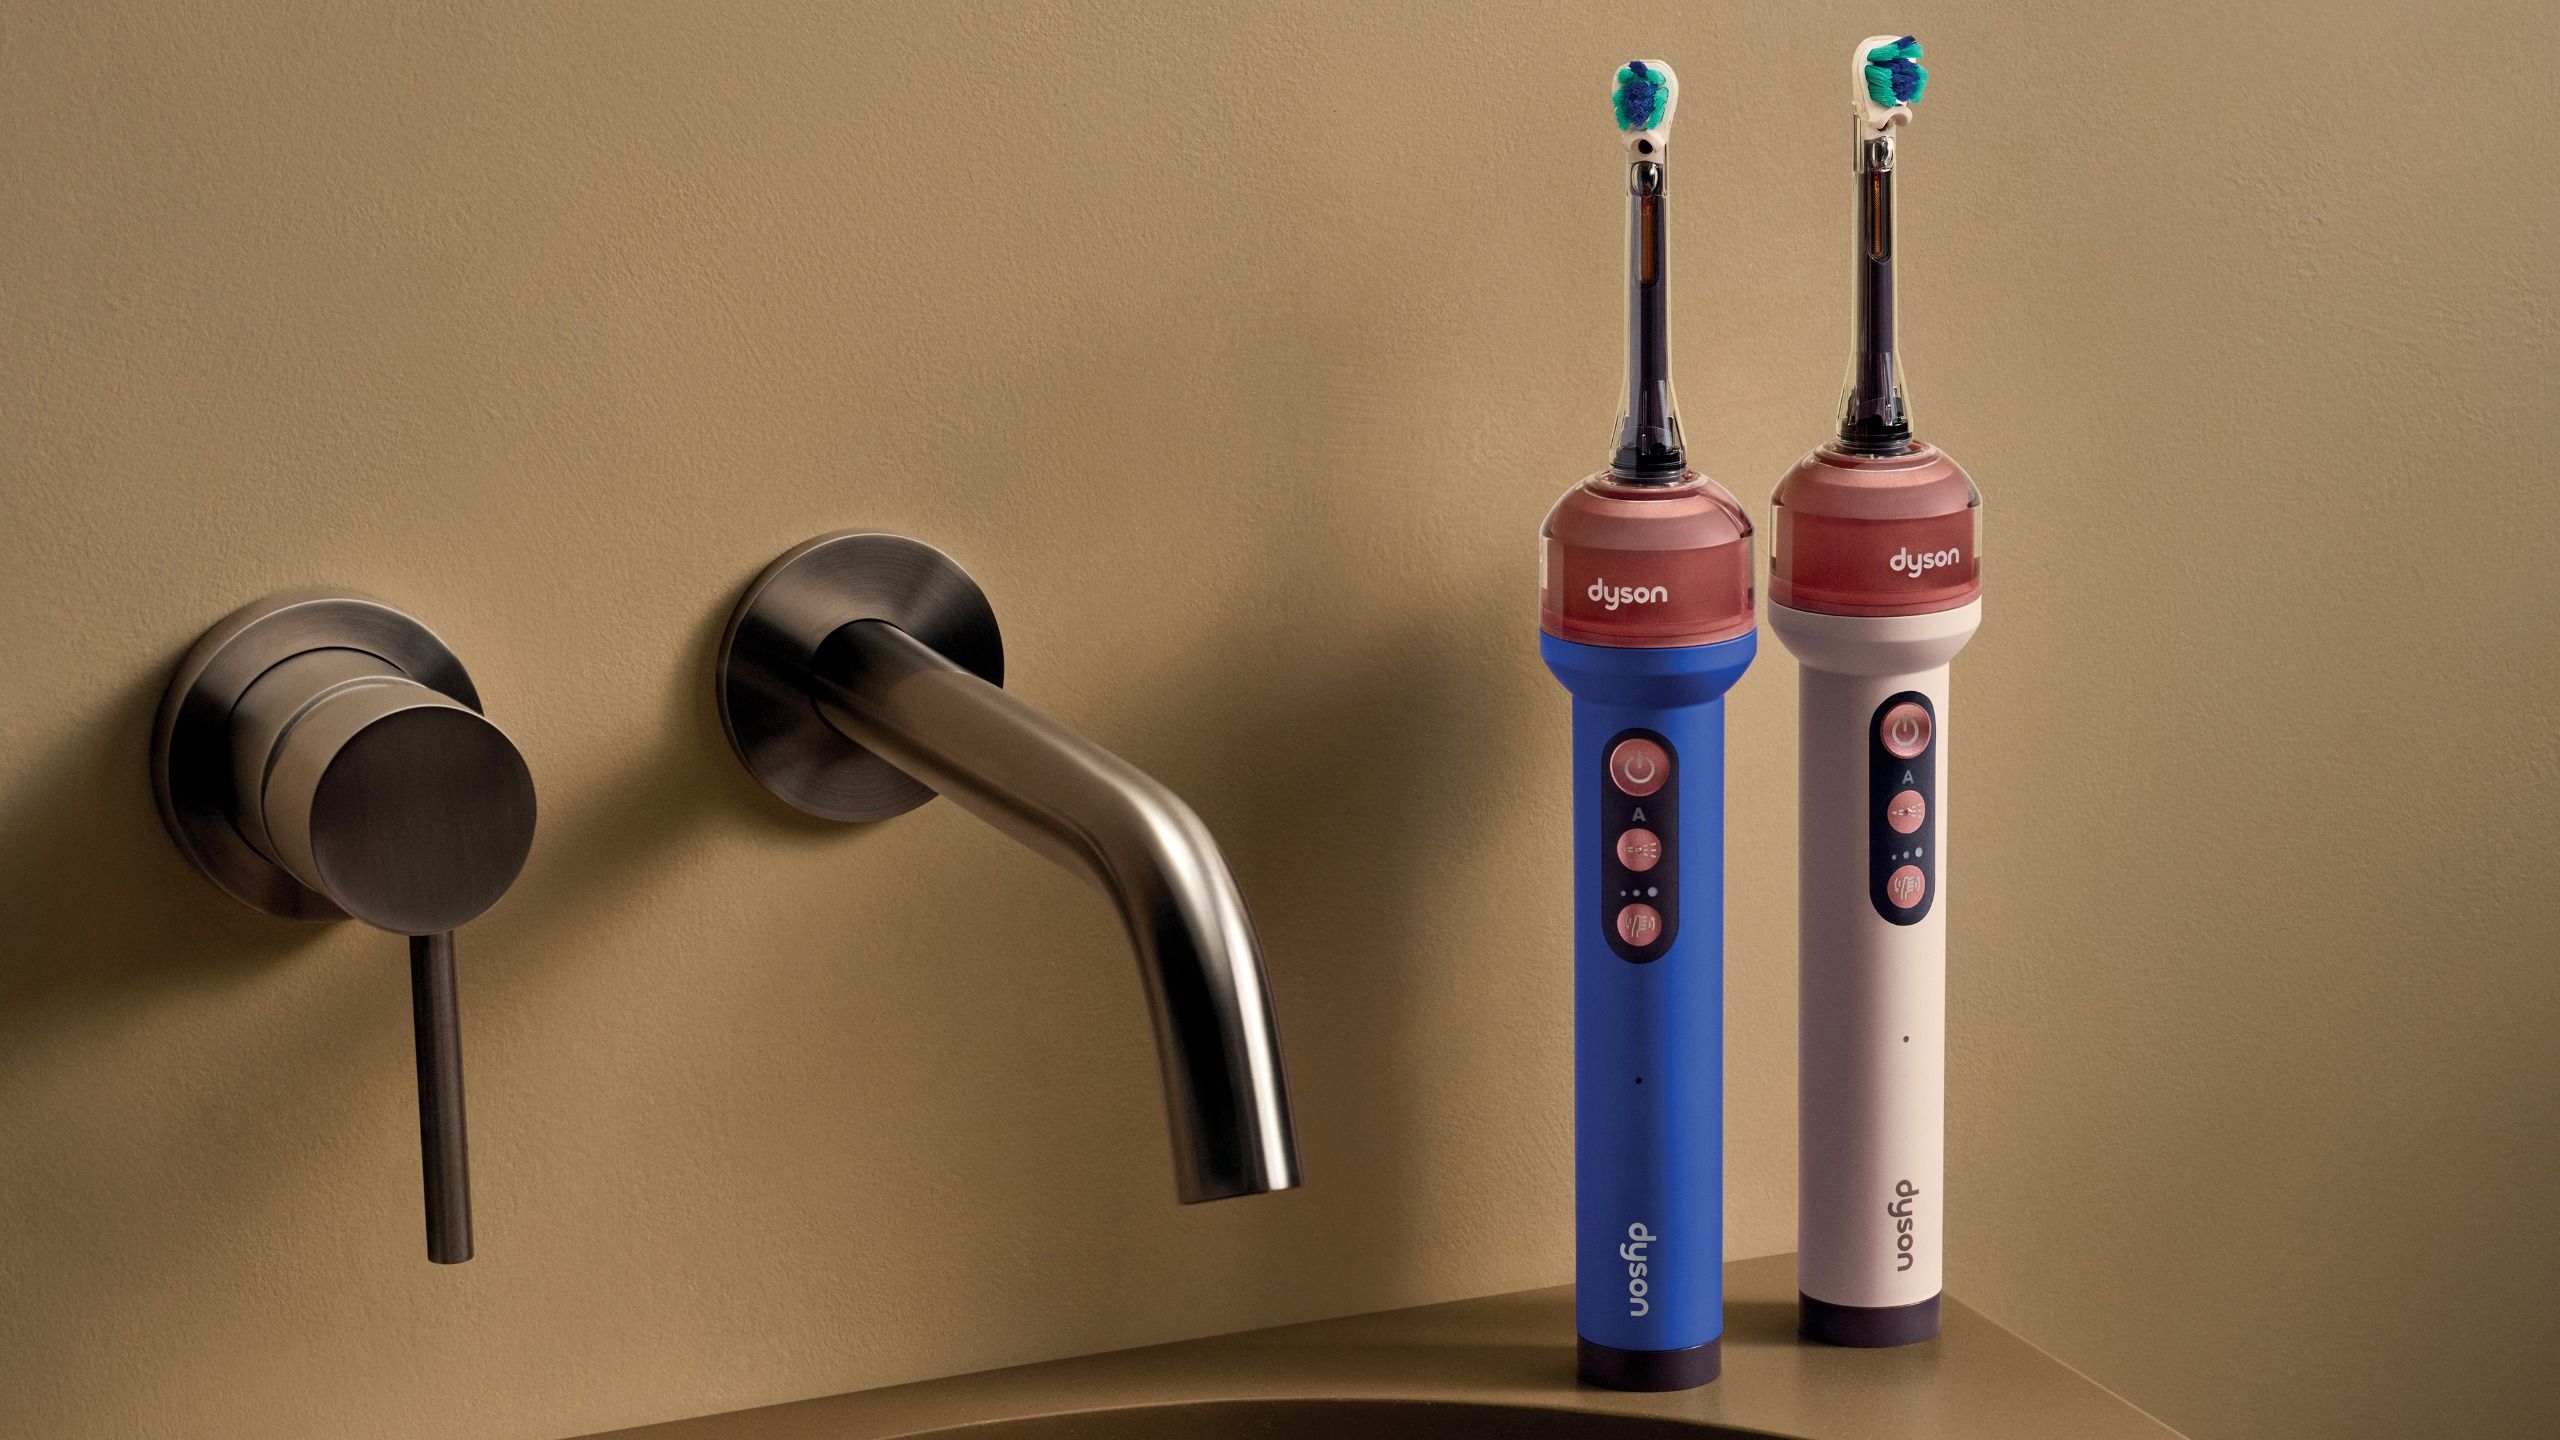
A camera in a toothbrush? Dyson tells us why it combined 'WiFi, AI, intelligent sensing and fluid dynamics with a highly engineered brushing experience' to create the Dyson Camerajet
WiFi, AI, and sensing in a toothbrush is another data-collection edge node disguised as a consumer device. If you build hardware, assume the bar is now closed-loop telemetry plus on-device intelligence, not just better mechanics.
 Applied AI
OpenAI Reportedly Trying to Solve Hodge Conjecture Amid Feud With Math Community
Frontier labs leaning into millennium problems is less about bragging rights and more about signaling that their models can handle deep, formal reasoning. If this pattern holds, expect pressure on research-heavy enterprises to treat LLMs as collaborators on core theory work, not just tooling around the edges.