

Suspected Chinese hackers posed as US AI insiders, Proofpoint says
THE SO WHAT
AI policy and research communities are now direct targets for nation-state phishing using insider impersonation. Lock down email, enforce strong identity checks for policy discussions, and treat AI governance mailing lists like high-value infrastructure.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
UK faces the most state-sponsored cyberattacks in Europe as AI narrows the attack timeline from days to minutes
State-backed attackers compressing timelines from days to minutes with AI means your detection and response loops have to be machine-speed too. CISOs in high-target regions like the UK need to move budget from static perimeter tools to continuous monitoring, automated triage, and rehearsed incident playbooks.
 Deep & Emerging Tech
Circle Logistics targets food and beverage shippers in reefer LTL service expansion
Consolidated cold-chain LTL run entirely through brokerage is another step toward networked, on-demand reefer capacity instead of fixed contracts. Food and beverage shippers should be mapping SKUs and lanes that can move to this model to claw back margin and resilience.
 Deep & Emerging Tech
'It is possible that threat actors are finding it more accessible or efficient to use LLMs and AI tools': Google warns that AI explosion will lead to more dangerous and advanced security threats
If attackers are using LLMs to better exploit known flaws, your patch latency and misconfigurations just became the primary AI-era attack surface. Security teams should assume exploit development is accelerating and prioritize hygiene and exposure management over chasing zero-days.
 Deep & Emerging Tech
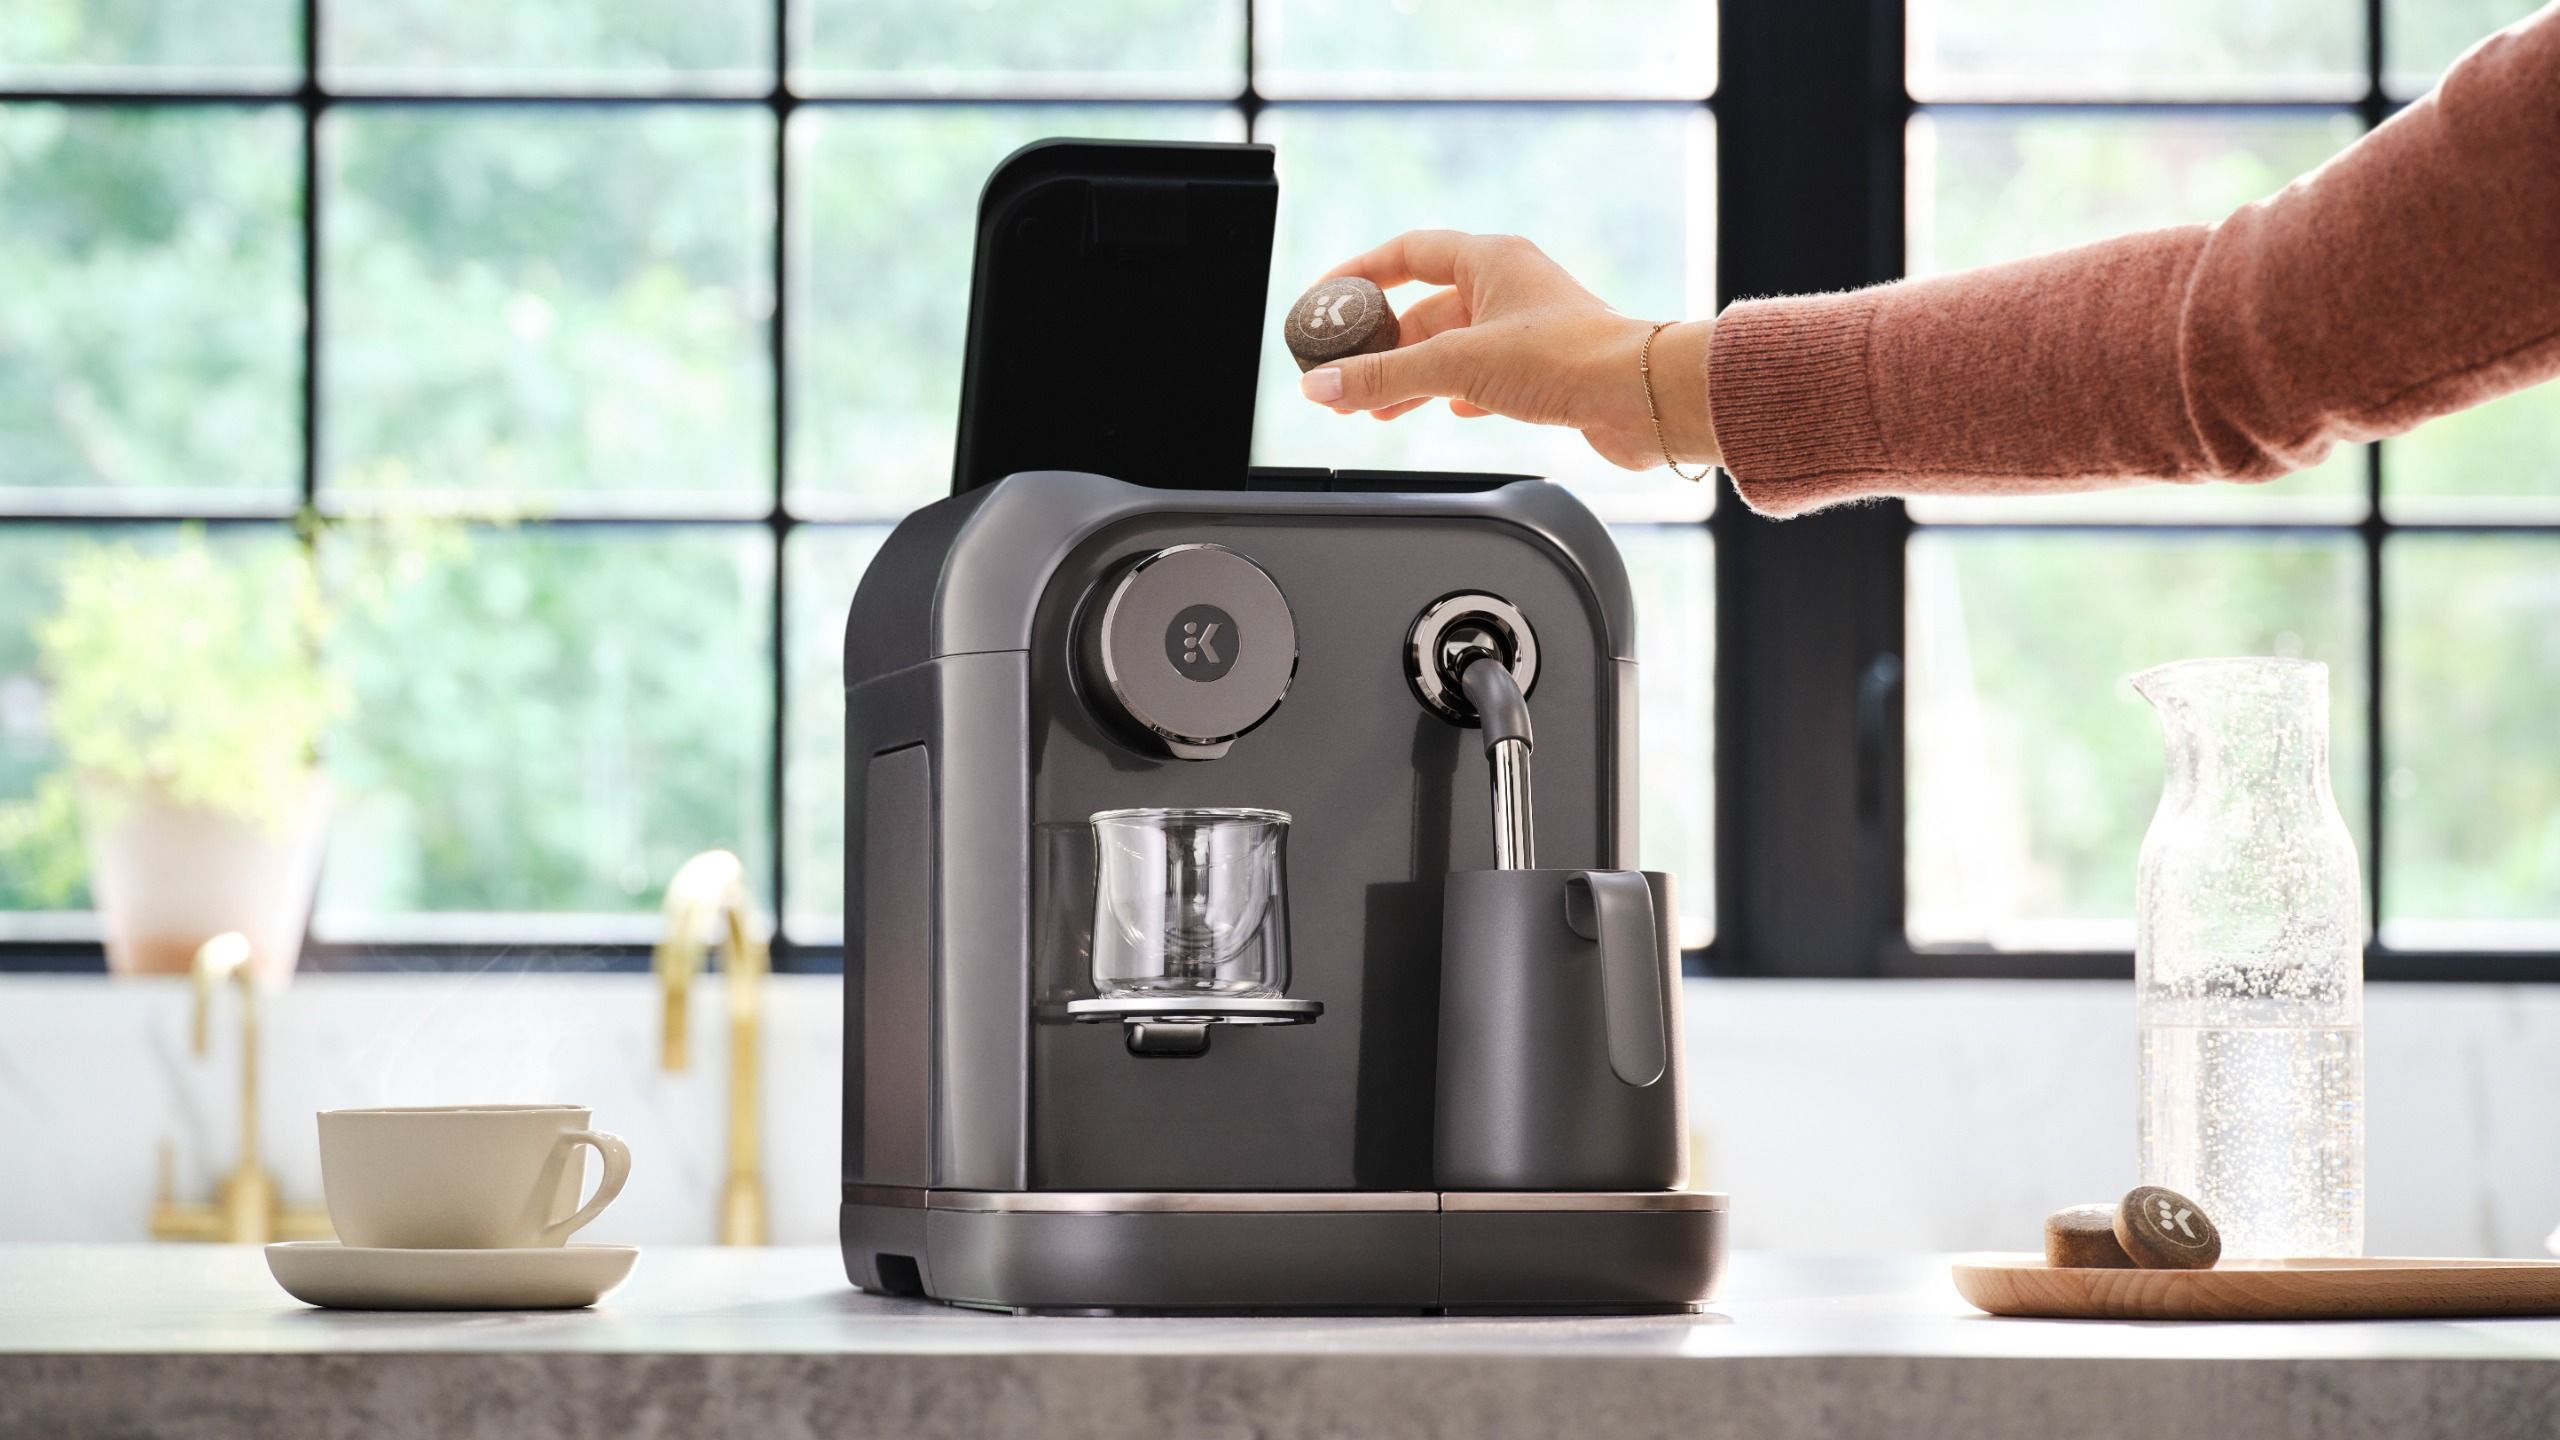
Keurig Alta system swaps plastic pods for compressed coffee tabs
Keurig shifting from plastic K-Cups to compostable coffee tabs is a material change in both waste profile and supply chain. CPG and appliance players should expect consumer and regulatory pressure to push more formats toward this kind of integrated sustainability redesign, not just packaging tweaks.