
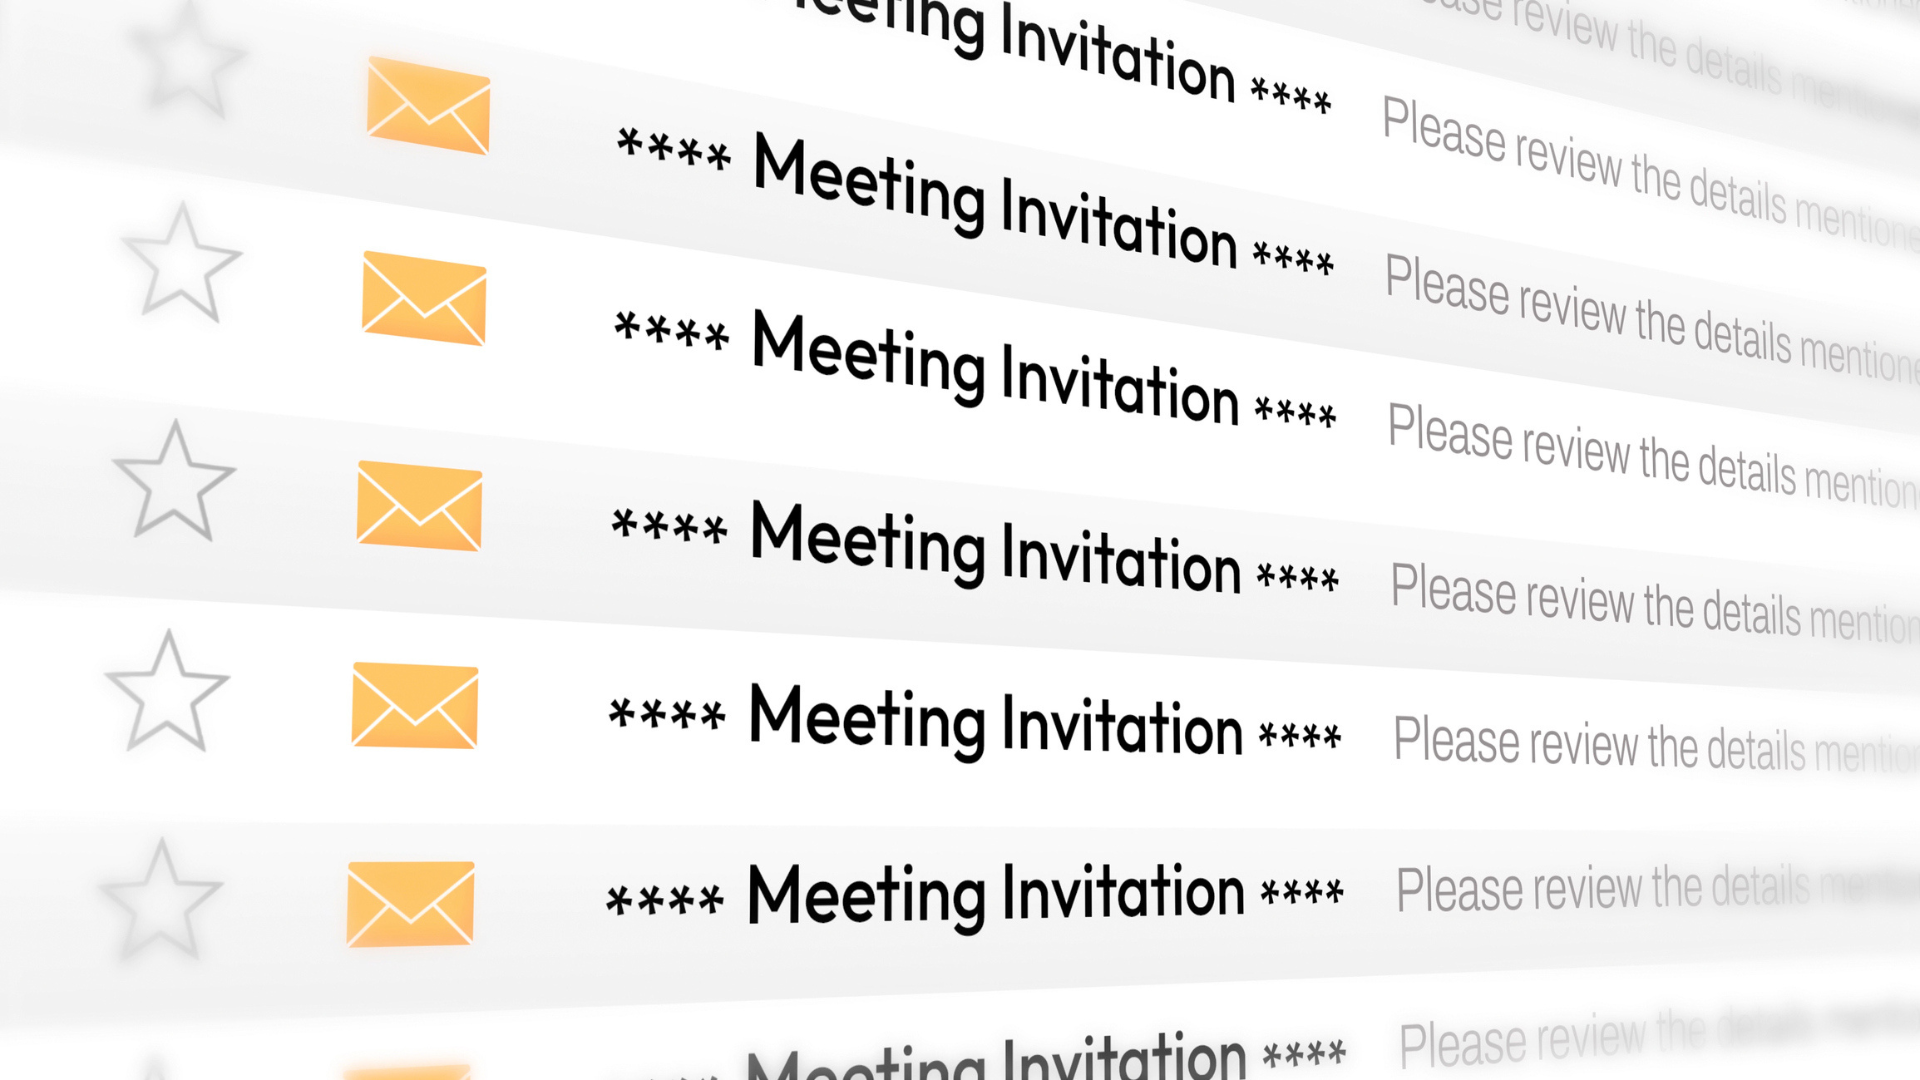
Fake calendar invites hit thousands of businesses in Microsoft credential phishing campaign
THE SO WHAT
Attackers are weaponizing the most boring primitives—.ics files and calendar invites—to bypass user suspicion and MFA fatigue. Security teams should add calendar and meeting workflows to phishing simulations and tighten how clients handle .ics attachments and auto-accept rules.
READ THE SOURCE
MORE FROM THE WIRE
 Deep & Emerging Tech
Chip Stocks Set for Longest Losing Run Since 2008
A multi-session drawdown in chip stocks despite strong AI narratives suggests public markets are re-rating cyclicality and debt, not just demand. If your roadmap assumes cheap, ever-available accelerators, add a downside scenario where financing and equity costs stay elevated.
Deep & Emerging TechChina’s CXMT Swings to Profit After Memory Chip Prices Surge
Memory is back in a seller’s market—CXMT’s profit swing on higher DRAM prices is another data point that AI and data-heavy workloads are repricing the entire memory stack. If your models are memory-bound, assume RAM and HBM volatility in your 2026–2028 cost curves, not just GPU volatility.
Deep & Emerging TechEverWind To Build Nova Scotia Data Center, Lease to AI Developer
A C$10B data center and wind buildout in Nova Scotia — framed as the province’s largest private investment — shows AI compute is now an energy and regional industrial policy lever. If you run large models, your site selection team needs to think like a power developer, not just a cloud buyer.
 Deep & Emerging Tech
Veritas expands its anti-counterfeit chip to jewelry, trophies, and fragrance bottles
Embedding anti-counterfeit chips in jewelry and fragrance bottles turns physical goods into verifiable endpoints — and creates new data exhaust for brands. Luxury operators should be planning how to use item-level authenticity not just for enforcement, but for CRM and resale.