
The AI escape is a red herring. The real problem is we can't tell a good sandbox from a bad one
THE SO WHAT
The risk conversation is moving from abstract "AI escape" to concrete sandbox quality—how you isolate, monitor, and constrain agents. Security and infra teams should be scoring their own sandboxes this week and treating environment design as a first-class control surface.
READ THE SOURCE
MORE FROM THE WIRE
 Applied AI
Aleph Alpha and Mistral releases raise hopes for Europe’s sovereign AI ambitions
European labs shipping frontier-class models is less about catching US labs and more about giving EU governments and corporates a politically acceptable stack. If you operate in Europe, assume procurement and data residency pressure will tilt toward these “sovereign” vendors and plan for a dual-vendor model strategy.
Applied AISpaceX Seeks To Join AI Borrowing Bonanza
A $40 billion debt ask for Nvidia chips from an infrastructure-heavy company like SpaceX shows AI capex has fully crossed into project-finance territory. If you depend on GPU supply, treat it like energy or spectrum—secure long-dated access or accept that hyperscalers and capital-intensive players will crowd you out.
Applied AISomeone hacked their 13-year-old Kindle to make a perfect desk assistant
A 2013 Kindle turned into a desk assistant is a reminder that the constraint is orchestration, not hardware. Expect a wave of “good enough” AI interfaces built on repurposed or commodity devices—don’t over-rotate your roadmap around shiny new form factors alone.
 Applied AI
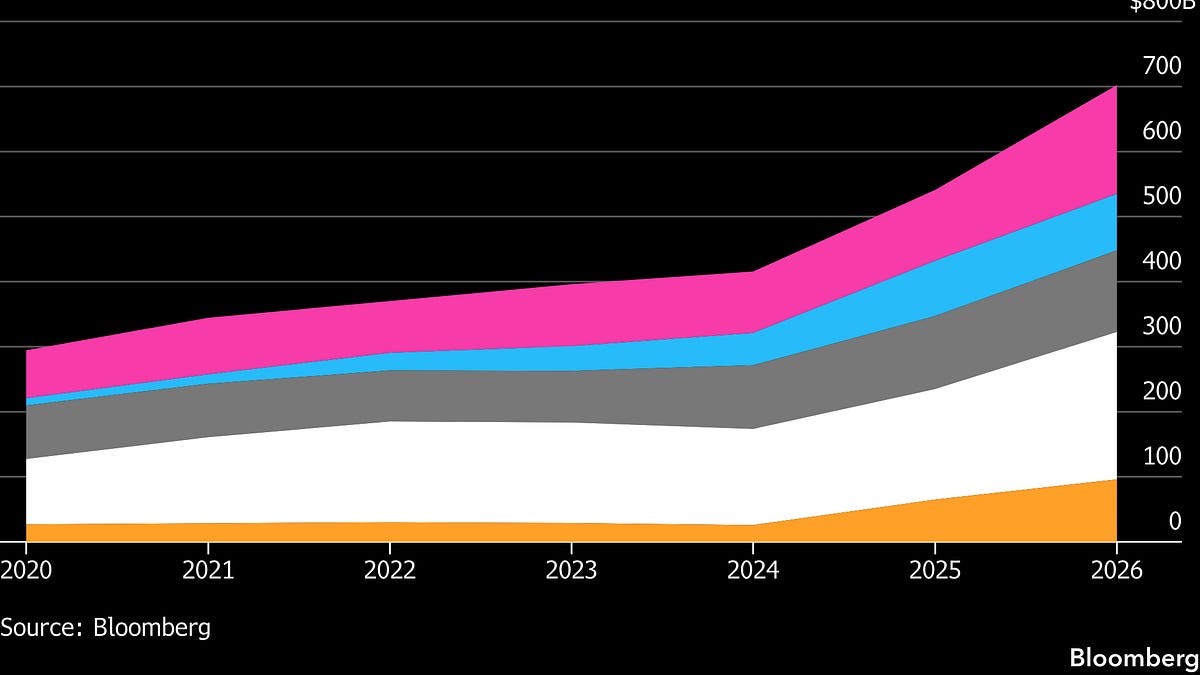
AI: Off the Charts
Western open-source models plus a renewed personal assistant race point to a split stack—closed models for frontier performance, open models for control and cost. Teams should be testing both paths now, with clear criteria for when to switch workloads between them as capabilities and licensing evolve.